
Enterprise Password Management
Secure enterprise credentials with Keeper's zero-trust password manager
Keeper's enterprise password manager verifies every access request, protects credentials with end-to-end encryption and enforces least privilege.
Keeper's enterprise password manager verifies every access request, protects credentials with end-to-end encryption and enforces least privilege.
Cybercriminals target credentials to gain entry into enterprise systems. Weak, reused and compromised passwords expose organizations to data breaches, ransomware attacks and mass account takeover.
Of tested enterprise environments had at least one password hash cracked in 2025
Of initial attack vectors for data breaches in 2025 were tied to credential abuse
Keeper's unified identity security platform gives organizations the visibility and control needed to secure credentials, enforce access policies and protect sensitive data across every user, device and system. Keeper is trusted by thousands of organizations worldwide, from SMBs to Fortune 500 enterprises and U.S. federal agencies.
Built on a zero-knowledge architecture, Keeper ensures complete data privacy through end-to-end encryption. All encryption and decryption occur locally on the user's device, meaning only the end user — not even Keeper — can view or decrypt the data.
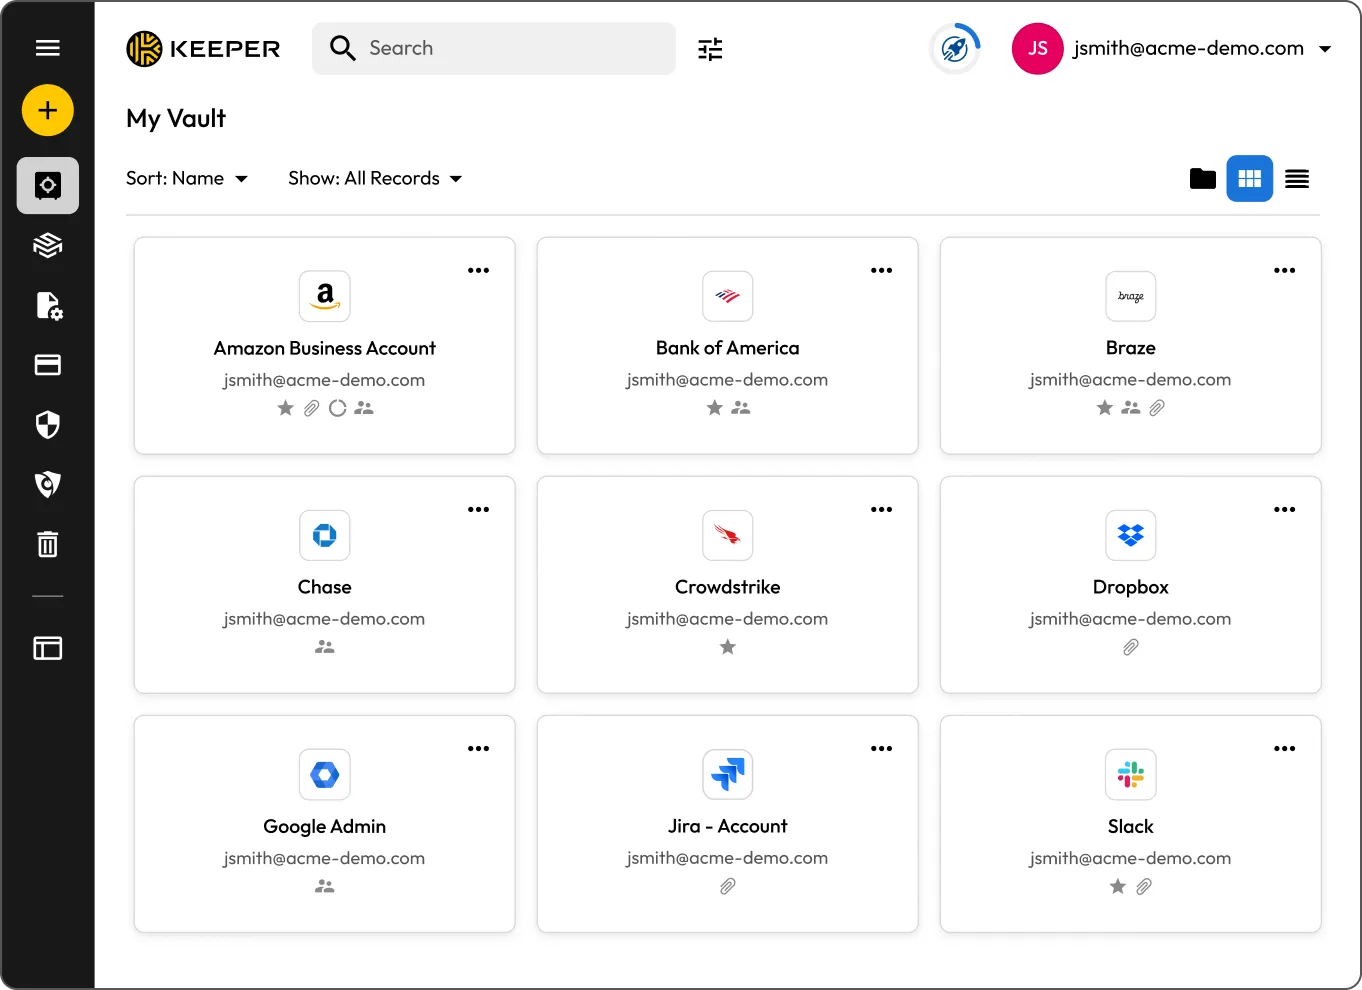
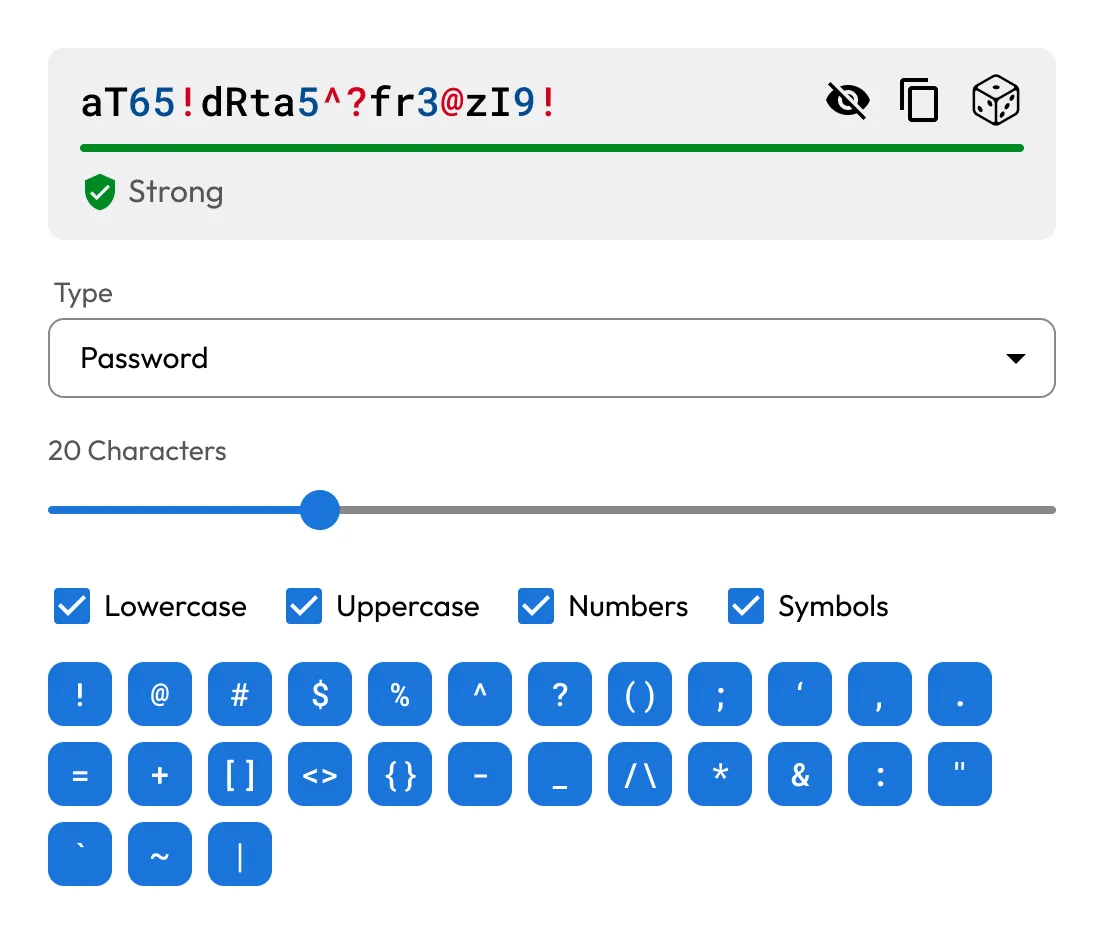
Every employee gets a private, encrypted vault to store passwords, passkeys, secrets and other sensitive data used by humans and machines alike. Keeper's built-in password generator and secure autofill work together to create and fill strong, unique passwords and passkeys, eliminating password reuse without adding friction.
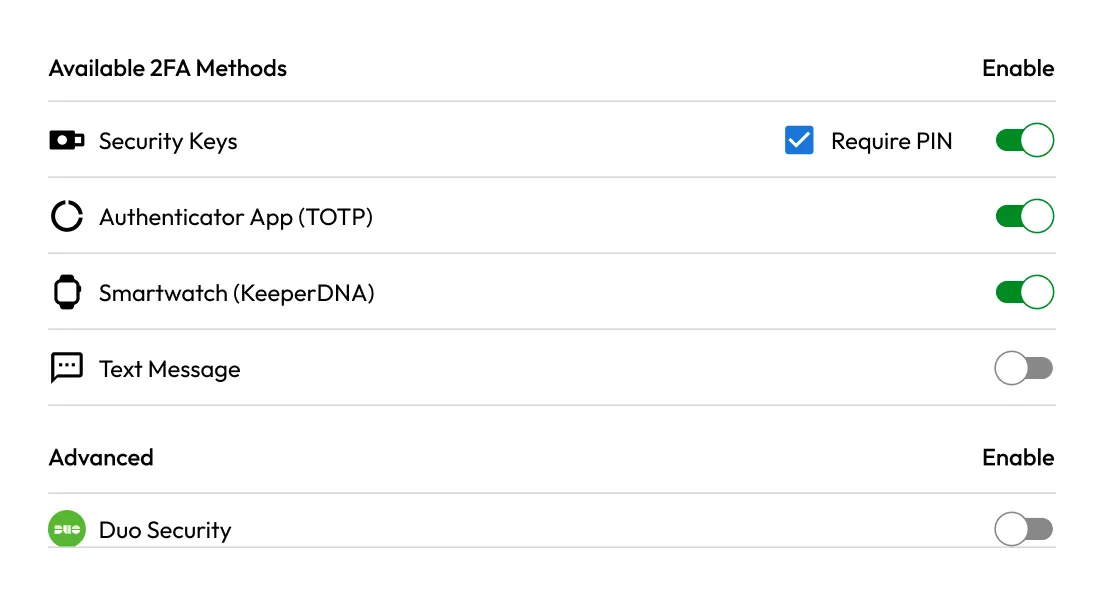
Keeper strengthens access security with support for multiple MFA methods, including TOTP, hardware security keys and biometrics.
With Keeper SSO Connect, organizations can enable passwordless authentication through their existing Identity Provider (IdP), ensuring secure access to the Keeper Vault. This helps reduce reliance on traditional passwords, tightening zero-trust security across all users and devices.
Keeper gives organizations precise controls over who can access what and when. By combining Role-Based Access Controls (RBAC) with Attribute-Based Access Controls (ABAC), along with time- and context-based restrictions, teams can enforce least privilege through intentional, granular policies across all users and systems.
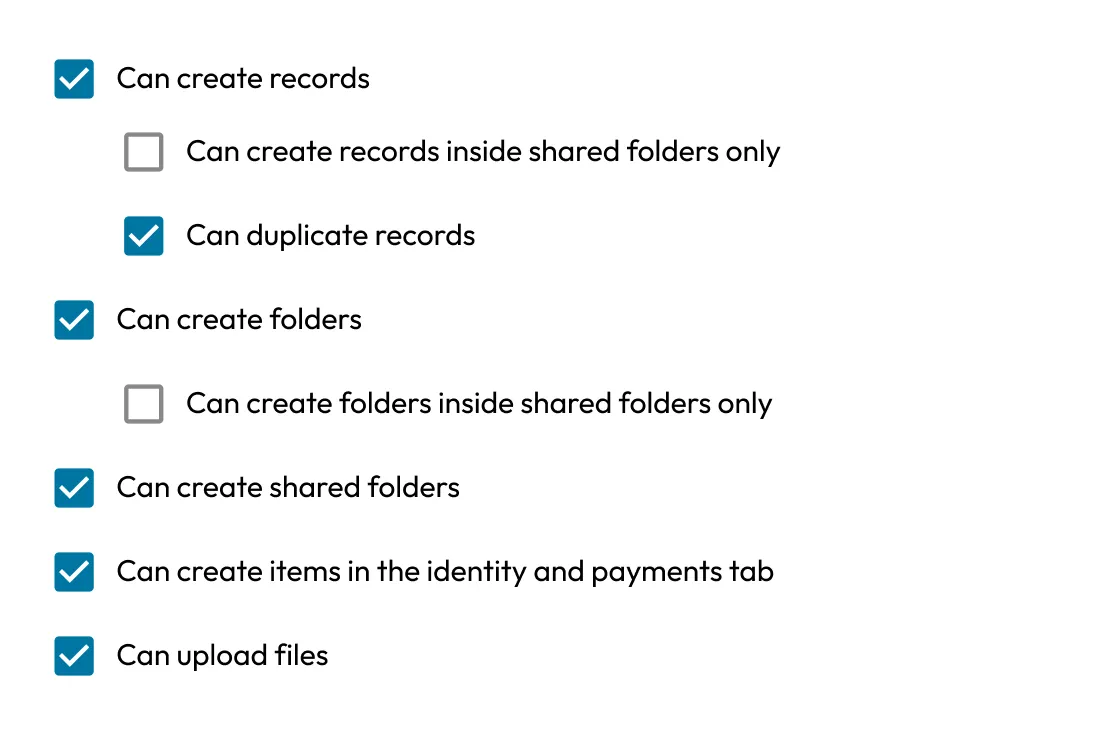
Keeper enables secure sharing of passwords and secrets through end-to-end encryption and granular access controls, making it easy for employees and third parties to collaborate without ever exposing sensitive data.
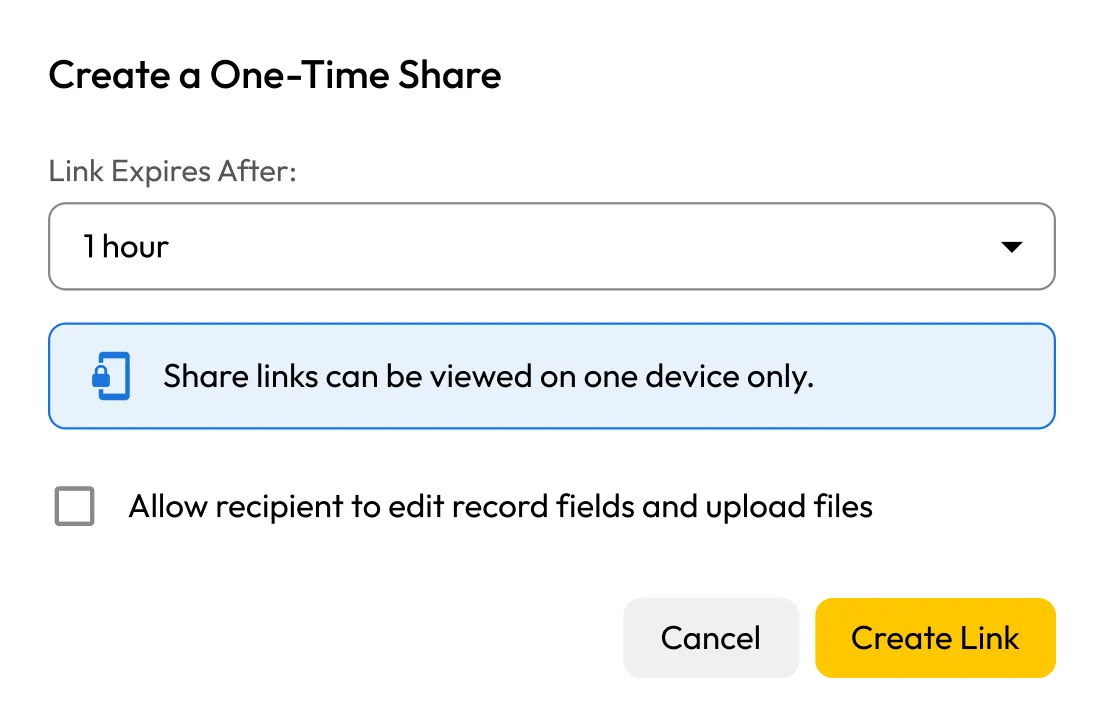
With One-Time Share, users can securely send credentials bound to a time limit, ensuring access to data automatically expires after use.
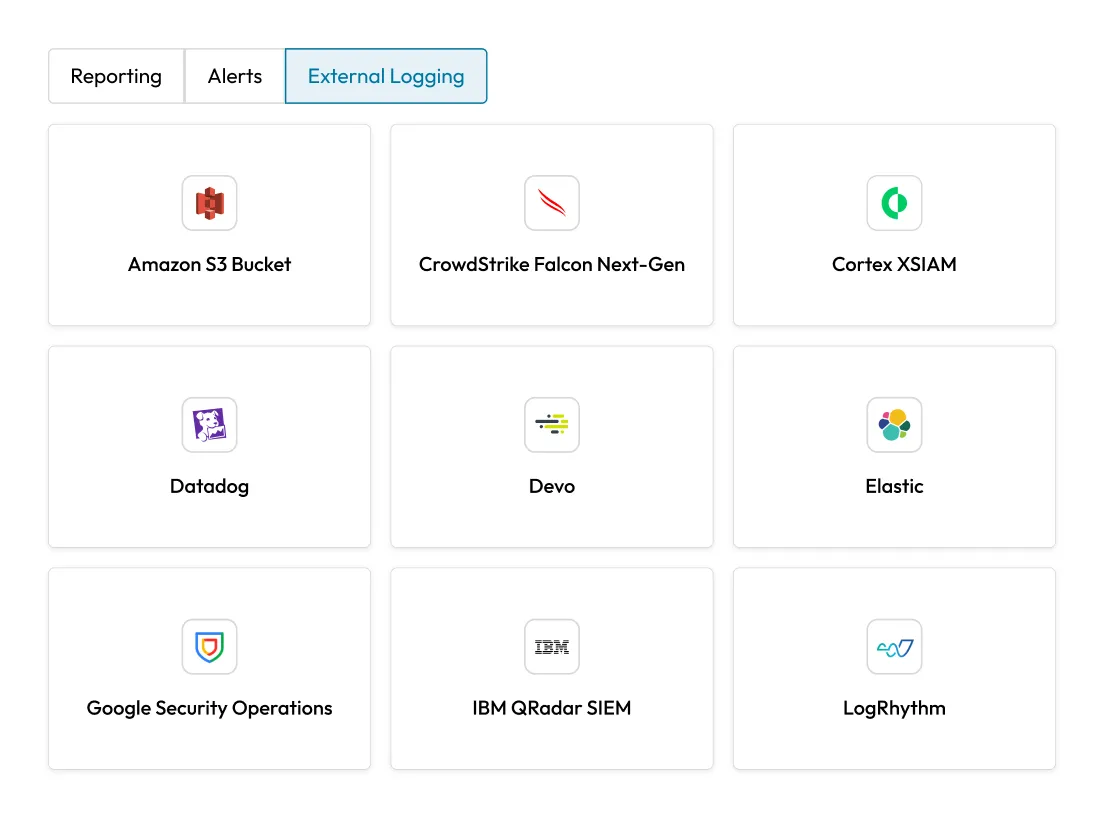
Keeper integrates seamlessly with your existing identity and security infrastructure, including IdPs like Microsoft Entra ID, Okta and Google Workspace; directory services like Active Directory and LDAP; and Security Information and Event Management (SIEM) tools. This enables fast deployment across on-premises, hybrid and multi-cloud environments.
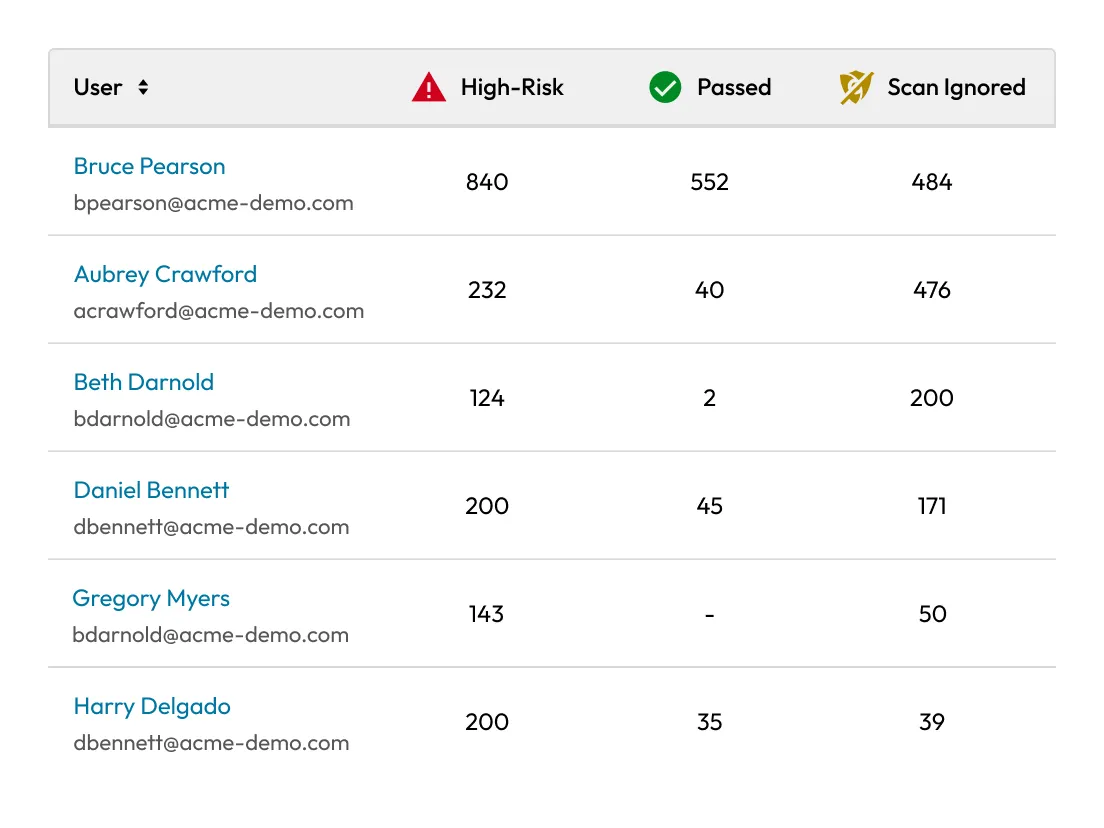
BreachWatch continuously monitors the dark web, scanning stored credentials against known compromised ones and alerting users in real time the moment a match is found. BreachWatch uses a zero-knowledge matching architecture. Credentials are anonymized before any comparison occurs, so neither Keeper nor any external service can see your plaintext passwords during the process. This gives organizations the visibility they need to respond quickly to credential exposure and stay ahead of account takeovers.
Keeper provides administrators full visibility into user activity through detailed audit trails, customizable reports and tracking across more than 300 event types. Keeper supports compliance with major frameworks like SOC 2 and ISO 27001, turning audit preparation from a burden into a straightforward, repeatable process.
Enterprise password management allows organizations to store, manage and share credentials securely across employees, departments and teams. It gives IT and security teams the ability to enforce strong password policies, reduce credential-based threats and gain full visibility into how access is managed across users, applications and systems.
Keeper simplifies enterprise password management by providing each user with their own secure, encrypted vault that automatically generates, stores and autofills credentials across devices and applications. With Keeper, users no longer need to rely on memory or reuse weak passwords. Features like autofill, secure sharing and passwordless authentication allow Keeper to streamline access while maintaining strong protection of credentials and data.
Keeper is a unified identity security platform that goes far beyond traditional password management. Not only does Keeper store and autofill passwords, but it also secures secrets, enforces granular access controls and offers Privileged Access Management (PAM) capabilities. Keeper also includes advanced security solutions like Remote Browser Isolation (RBI), endpoint privilege management and privileged session management, allowing organizations to control access, secure infrastructure and protect both human and machine identities.
Keeper gives security and IT teams full visibility and control over how credentials are used across their organization. Administrators can enforce RBAC, monitor user activity and generate detailed audit trails in real time. This oversight helps organizations respond to possible cyber threats more efficiently and maintain compliance with regulatory requirements.
You must accept cookies to use Live Chat.