
 PAM
Privileged Access Management (PAM) helps small businesses control, monitor and secure access to sensitive systems, administrator accounts and business-critical applications. It reduces the risk of credential
6 min read
Published on December 13, 2024
Updated on October 2, 2026.
The main difference between Identity and Access Management (IAM) and Privileged Access Management (PAM) is scope. IAM manages who has access to which resources across your entire organization, while PAM secures access to your most sensitive information. PAM falls under the umbrella of IAM by monitoring the small group of user identities with privileged access.
Continue reading to learn more about IAM and PAM, their key differences, what they have in common and when to implement each one in your organization.
What are IAM and PAM?
Identity and Access Management (IAM) helps your organization manage which employees can access specific resources and systems. IAM identifies users through their login credentials, controls access based on roles and grants access to systems based on certain permissions. Think of IAM as a key card at work; when you scan your card, you can enter the building and the specific rooms you have been granted access to based on your job.
So, what is privileged access management? Privileged Access Management (PAM) is a subset of IAM that secures and monitors access to your organization’s sensitive data. Privileged accounts handle your organization’s most sensitive information, including payroll or IT resources. Because of this, PAM monitors those accounts’ activities under stricter security controls than regular users. If IAM is like a key card at work, PAM is like a key card that grants access to a room containing highly confidential information.
IAM and PAM work together rather than separately. IAM establishes who every user is and what they’re allowed to access. PAM then adds another layer of protection for the accounts that hold elevated permissions, controlling and recording what those users do once they’re inside sensitive systems.
3 key differences between IAM and PAM
Despite PAM being a subset of IAM, there are several key differences between the two access management systems.
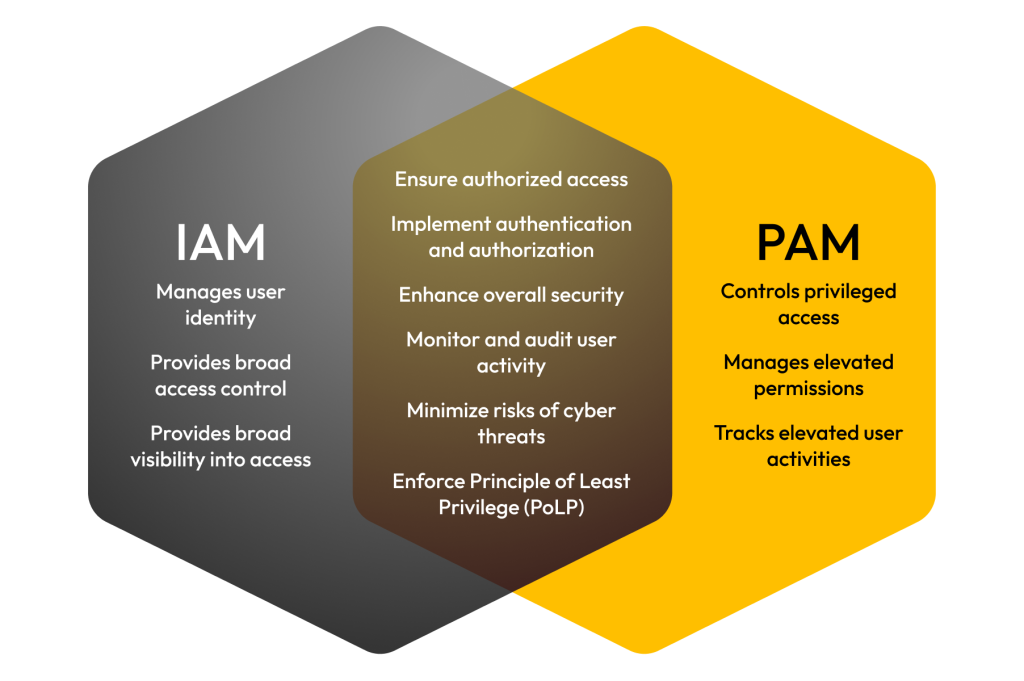
1. IAM manages user identity, whereas PAM controls privileged access
One of the main differences between IAM and PAM is which users they manage. IAM focuses on the identity of all users, and PAM focuses only on privileged accounts. IAM pays closer attention to user identities and their roles within an organization, analyzing factors like who a user is, which systems they should have access to and how they can access those systems. For example, IAM ensures that anyone in an organization can access necessary resources if they are in a certain location and/or during a certain time period, such as during business hours.
PAM manages and monitors privileged users’ access to critical systems, prioritizing accounts with higher-level permissions like administrators or IT team members. With PAM, your organization can control which employees receive privileged access, how long they can access sensitive systems and what they can do while they have that access. PAM keeps tight control over privileged accounts due to the power of the systems and resources they manage, helping to prevent data breaches of especially sensitive information.
2. IAM provides broad access control, whereas PAM focuses on elevated permissions
IAM provides and manages access for all users in an organization, offering broader access control compared to PAM, which focuses on privileged accounts. IAM ensures that all users have the correct permissions to do their jobs effectively without necessarily prioritizing those with privileged accounts.
PAM monitors user access to high-level administrative accounts, restricting who can access sensitive systems and enforcing strict controls on what users can do with sensitive information. With a PAM solution, your organization can monitor how privileged access is used through security features such as Just-In-Time (JIT) access, which allows users access to sensitive systems only for a specific time period to complete certain tasks.
3. IAM provides broad visibility into access, while PAM tracks elevated user activities
Think of IAM as access to a store containing merchandise of varying monetary value, with PAM being access to the most valuable merchandise in the store, such as very expensive jewelry kept behind a locked counter. IAM gives your organization visibility into the big picture of all your employees, systems, access and permissions. For example, IAM can be used to see if an employee has access to a specific app and ensure everyone has the right access to general information needed based on their role.
PAM provides detailed tracking and auditing of privileged users’ activities. For example, PAM is used to monitor the activities of IT and security administrators at your organization. PAM tracks what each administrator is doing with their privileged permissions because the data and systems they have access to are more sensitive than what regular employees can access.
What do IAM and PAM have in common?
IAM and PAM differ in scope, but they share the same main purpose: making sure the right people have the right access to the right resources. Both rely on authentication and authorization to verify users and approve what they can do. Understanding the difference between authentication and authorization helps clarify how each system makes access decisions. Both also help organizations implement the principle of least privilege, so users receive only the access they need. Below shows more on what IAM and PAM have in common.
| What IAM and PAM have in common | How IAM applies it | How PAM applies it |
|---|---|---|
| Ensure authorized access | Verifies that every user can reach only the resources their role needs | Ensures only approved users can reach privileged accounts and sensitive systems |
| Implement authentication and authorization | Authenticates all users and authorizes access based on roles and policies | Applies stronger verification to privileged sessions and authorizes privileged actions task by task |
| Enhance overall security | Reduces access-related risk across the entire workforce | Protects the high-value accounts cybercriminals target most |
| Monitor and audit activity | Logs sign-ins and access changes for all users | Records and audits privileged sessions in detail |
| Minimize risks of cyber threats | Helps prevent unauthorized access from stolen or misused credentials | Limits the damage a compromised privileged account can cause |
| Enforce least privilege | Grants each user the minimum access needed for their role | Restricts elevated permissions to only when and where they're needed |
When to implement IAM vs PAM in your organization
Typically, organizations should implement both IAM and PAM, depending on the types of users and data they have.
When to implement IAM
Your organization should implement IAM if the following scenarios apply:
- Managing general user access: IAM should be implemented when you need to determine who can access specific resources within your organization, whether you’re a new organization or are growing rapidly. With IAM, you can control which users have certain access, reducing the risk of data breaches.
-
Broad user access management across your organization: If your organization has a wide range of users who need access to various systems, IAM can assist in assigning permissions based on user identity on a larger scale. This ensures every user has the correct access to systems while reducing the risk of human error when updating permissions manually.
When to implement PAM
Your organization should implement PAM if the following scenarios apply:
- When you need to control, monitor and audit privileged access: If your organization needs to limit who can use privileged accounts, monitor what users with privileged access do and audit their activity, you should implement PAM. This will ensure that only authorized users can access sensitive information and provide a record of activity in sensitive systems.
-
When monitoring and auditing elevated user activities: Elevated users have access to some of your organization’s most important information, so implementing PAM will help you track and review their activities. PAM ensures privileged users are engaging in authorized activities by providing real-time visibility into privileged user activity and audit trails.
Deploy IAM and PAM with Keeper
It’s not a question of which will better protect your organization; IAM and PAM are both essential and work hand-in-hand to secure access for every account. The most effective approach is a platform that covers both, so you don’t have to use several separate tools for everyday users and privileged accounts. Keeper supports IAM and PAM in a single zero-trust, zero-knowledge platform. On the IAM side, Keeper helps your organization manage access for every user, helping secure credentials, enforcing strong authentication and applying role-based policies across your workforce. On the PAM side, KeeperPAM is a cloud-based privileged access management solution that protects your most sensitive accounts with password and secrets management, privileged session management, Just-in-Time (JIT) access and automated credential rotation.
Start your free trial of KeeperPAM today to experience full visibility and control over privileged user activity in your organization.
Frequently asked questions
What is IAM vs PAM vs PIM?
IAM manages identities and access for every user in your organization. PAM and Privileged Identity Management (PIM) are both subsets of IAM that focus on privileged accounts, but they address different parts of privileged access. PIM manages which identities hold privileged roles and for how long. PAM secures and monitors how those accounts are used once they have privileged access. Read our blog to learn more about PIM vs PAM.
What modern PAM tools integrate with cloud IAM?
Modern PAM tools are typically cloud-based and designed to integrate with the cloud IAM and Identity Providers (IdPs) organizations already use. When evaluating PAM tools, look for support for Single Sign-On (SSO) through standards like SAML 2.0, automated user provisioning through SCIM and integration with major IdPs and cloud platforms. These integrations allow you to manage privileged access using the same identities and policies you’ve set up in your IAM system. KeeperPAM is a cloud-native PAM solution that integrates with leading IdPs, so your organization can extend IAM policies to privileged accounts without adding more complexity.
What are the key differences between IAM, IGA and PAM?
IAM controls who can access which resources and how users authenticate. Identity Governance and Administration (IGA) adds a governance layer on top of IAM, focusing on managing the identity lifecycle, running access reviews and ensuring access policies meet compliance requirements. PAM focuses specifically on securing, monitoring and auditing privileged accounts. Simply put, IAM manages access, IGA governs that access and PAM protects the most sensitive access. Learn more about the differences between IAM and IGA.

