
 PAM
Privileged Access Management (PAM) helps small businesses control, monitor and secure access to sensitive systems, administrator accounts and business-critical applications. It reduces the risk of credential
There is no single schedule for privileged user access reviews; organizations should set their cadence based on their risk profile and applicable compliance requirements. As a risk-based reference point, CISA recommends reviewing privileged accounts at least quarterly and reauthorizing access annually for federal High Value Assets. Organizations may choose to review especially sensitive accounts, such as domain administrator and root accounts, monthly.
Continue reading to learn why regular privileged access reviews matter, explore review best practices and see how KeeperPAM can streamline the process.
Why privileged user access reviews matter
Reviewing privileged access regularly reduces security risk by making sure only authorized people can reach the resources they need. It also prevents privilege creep, the slow accumulation of permissions over time. An engineer gets production access for a migration and keeps it after the migration ends. A contractor is added to an admin group and never removed. Each one looks harmless on its own, but together they create an attack surface nobody on your team can describe from memory. An account carrying three years of accumulated permissions gives an attacker far more room to move laterally than one scoped to its current job.
Without ongoing oversight, outdated or excessive privileges may remain in place, increasing the likelihood of unauthorized access and misuse of sensitive data. Reviews also protect you at audit time. Frameworks don’t just ask whether you control privileged access. They ask you to prove you verify it on a schedule.
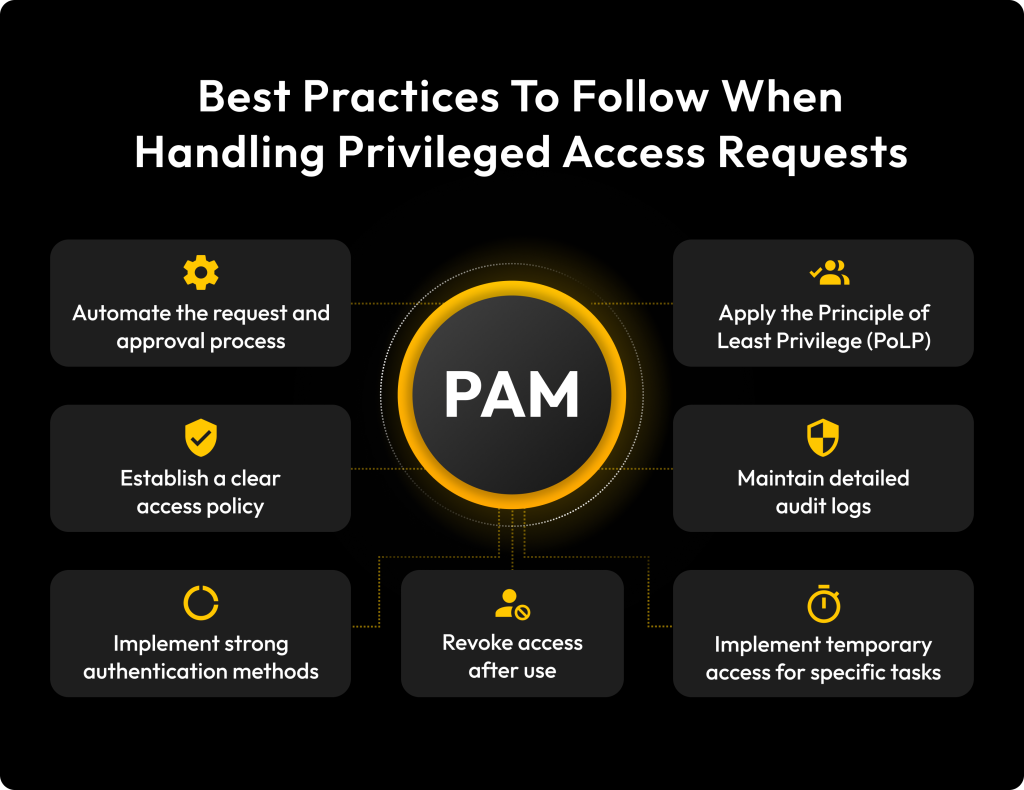
Best practices for reviewing privileged access
When reviewing privileged access, organizations should follow these best practices to maintain security and compliance.
Run periodic access review cycles
Reviewing privileged accounts at least once a quarter helps you identify over-privileged accounts and close security gaps. Pair it with a comprehensive review at least once a year to stay aligned with industry standards and limit privilege creep.
If you are asking how often you should review security settings more broadly, align them with your access review cycle. Reviewing entitlements quarterly while leaving password policies, MFA enforcement and session timeout rules untouched for two years leaves an obvious gap. Audit the controls and the permissions in the same pass.
Monitor and log in real time
Periodic reviews matter for long-term security, but privileged account misuse can happen at any time. Recording and tracking user activity lets you detect suspicious behavior, unauthorized access and policy violations before they cause significant damage. Audit trails give you a detailed record of privileged access and account activity, which holds users accountable and supports ongoing compliance.
Review access after major changes
Review privileged access whenever something significant changes, such as an employee leaving, changing roles or a system update or merger. These events shift access needs, and leaving access rights unchanged can leave unnecessary permissions in place.
How KeeperPAM® streamlines privileged access reviews
A Privileged Access Management (PAM) solution like KeeperPAM simplifies the review process. It provides a centralized dashboard, supports granular access control, enables session management and automates compliance and audit reports.
Get centralized access visibility
The Keeper Admin Console gives administrators a single place to see who has access to what. From the console, you can view every user, team and role in your organization, see which shared folders and records each one can reach, and check the permission level on each. You can also see which enforcement policies apply to each role and which users have not yet enrolled in MFA.
Use granular access controls
KeeperPAM supports both Role-Based Access Controls (RBAC) and Just-in-Time (JIT) access, enabling organizations to implement granular access controls that align with their security policies. With RBAC, entitlements are assigned at the role level rather than user by user. You define a role, attach the policies and shared folder access it needs, then add users. Anyone in that role inherits exactly that access and nothing else, so when someone changes jobs, you move them to a different role and their old permissions go with it. This also shortens your reviews. Instead of auditing permissions for every individual user, you audit the roles, then confirm role membership is correct.
JIT covers the cases where someone needs elevated privileges but shouldn’t keep them. Users request access for a specific task, access is granted for a set window and it expires on its own. Nobody has to remember to revoke it. The combination of these two approaches optimizes access management and significantly reduces the potential for privileged account misuse.
Monitor and record sessions
KeeperPAM’s privileged session management lets admins to monitor, record and control privileged sessions in real time. KeeperPAM captures every action performed by a privileged user, from full screen recordings to keystroke-level detail for SSH and database sessions. Recordings are stored encrypted and can be played back later for investigation, compliance evidence or review.
Session events also stream to any Security Information and Event Management (SIEM) tool. KeeperPAM supports Splunk, Microsoft Sentinel, Datadog, Sumo Logic, Syslog and generic webhooks, so privileged activity shows up in the same place your security team already watches. If an account starts behaving unusually between scheduled reviews, your existing detection rules catch it rather than waiting for the next quarterly cycle.
Automates compliance and audit reporting
KeeperPAM reduces the complexity of meeting compliance standards like FedRAMP, SOC 2, ISO 27001 and HIPAA by automatically generating detailed audit logs and compliance reports. Every privileged access event is recorded, including vault logins, record access, permission changes and session starts. The worth of an audit trail can be illustrated by the difference between telling an auditor you control privileged access and showing them. These reports provide a comprehensive record of privileged access activities, ensuring that every periodic access review is fully documented and demonstrating adherence to standards. By automating compliance reports, organizations can streamline the auditing process, minimize manual effort and ensure timely and accurate reporting for audits.
Simplify privileged user access reviews with KeeperPAM®
Periodic privileged access reviews and following best practices are necessary for strengthening an organization’s security infrastructure. However, these regular processes become much easier with the right PAM solution in place.
KeeperPAM offers the ideal solution with its unified, user-friendly platform. With key features like JIT access, RBAC, advanced monitoring and auditing capabilities, KeeperPAM simplifies the secure management and control of privileged accounts, providing peace of mind for your organization.
Request a demo of KeeperPAM today to streamline privileged access reviews and maintain a strong security posture for your organization.

