Govern and manage privileged access
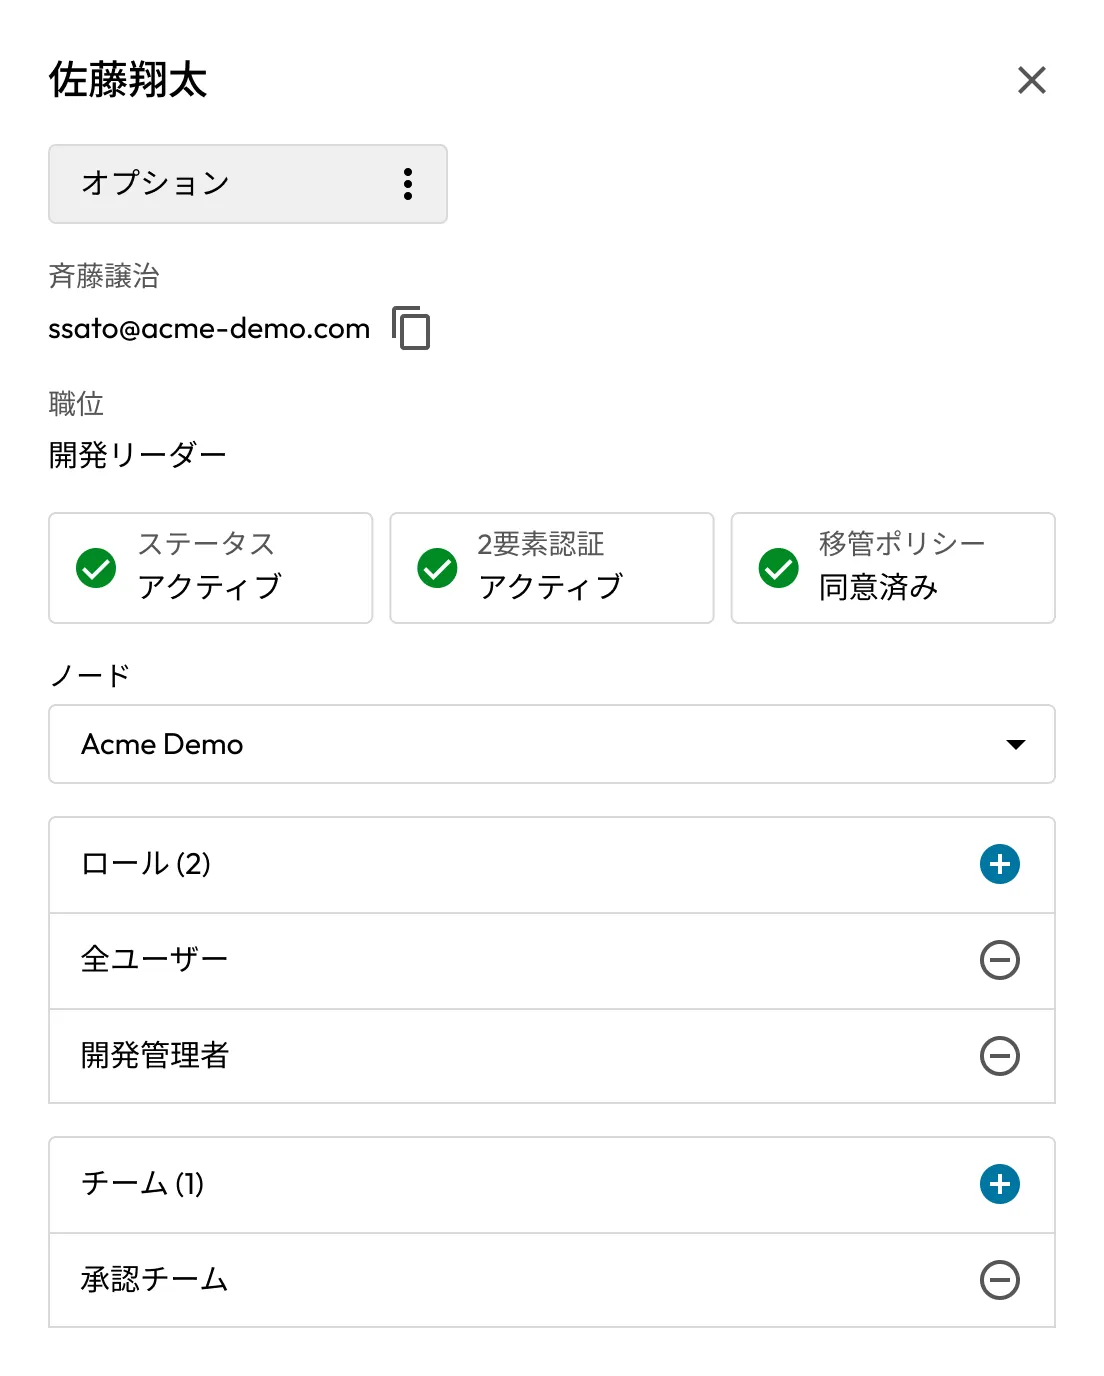
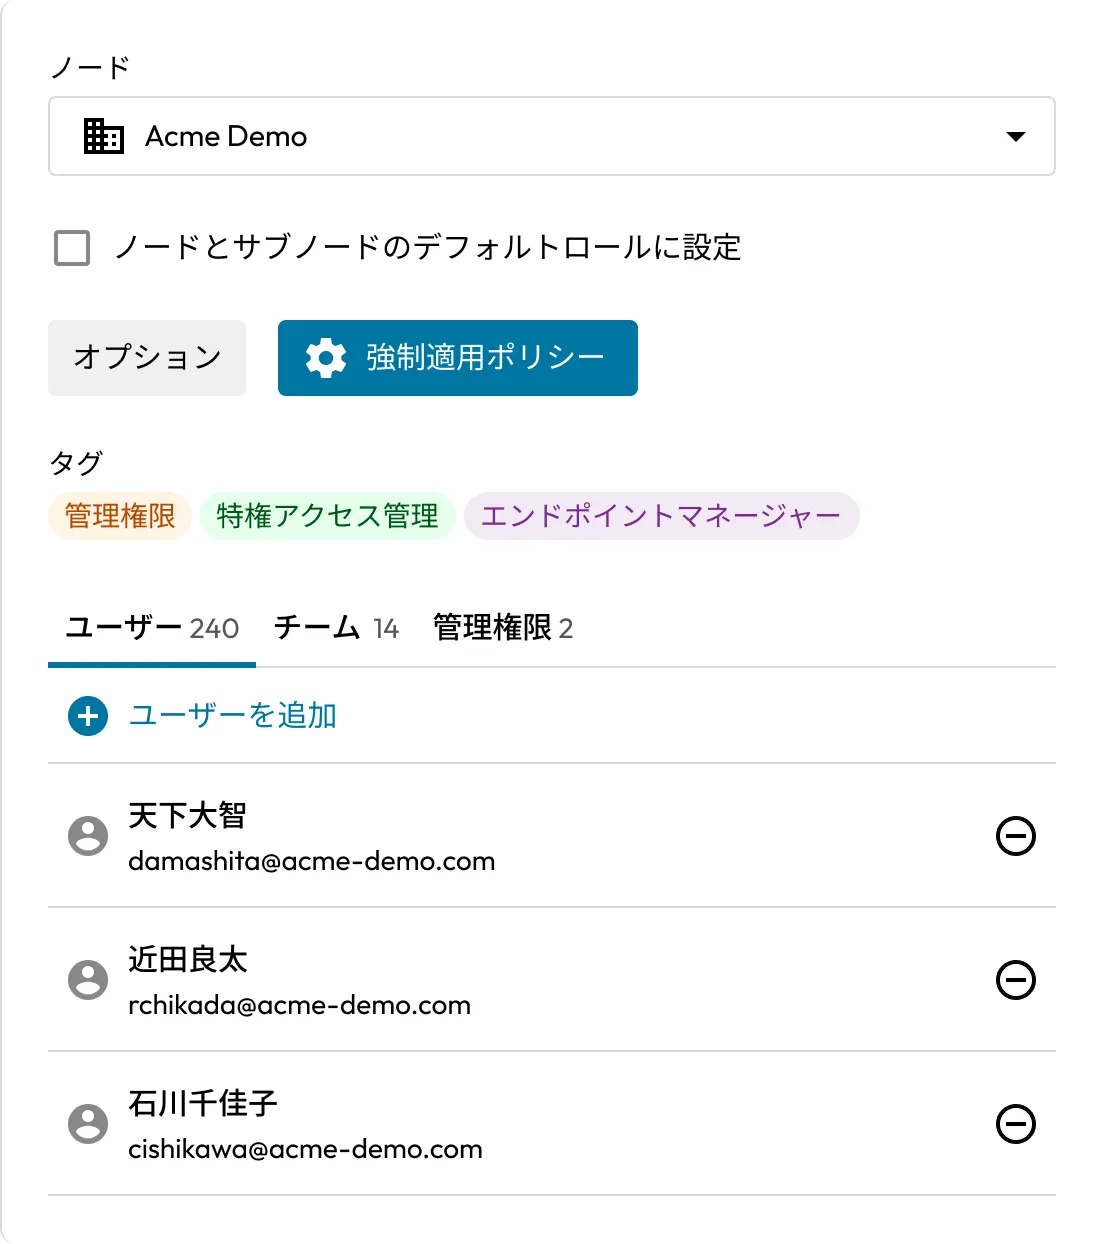
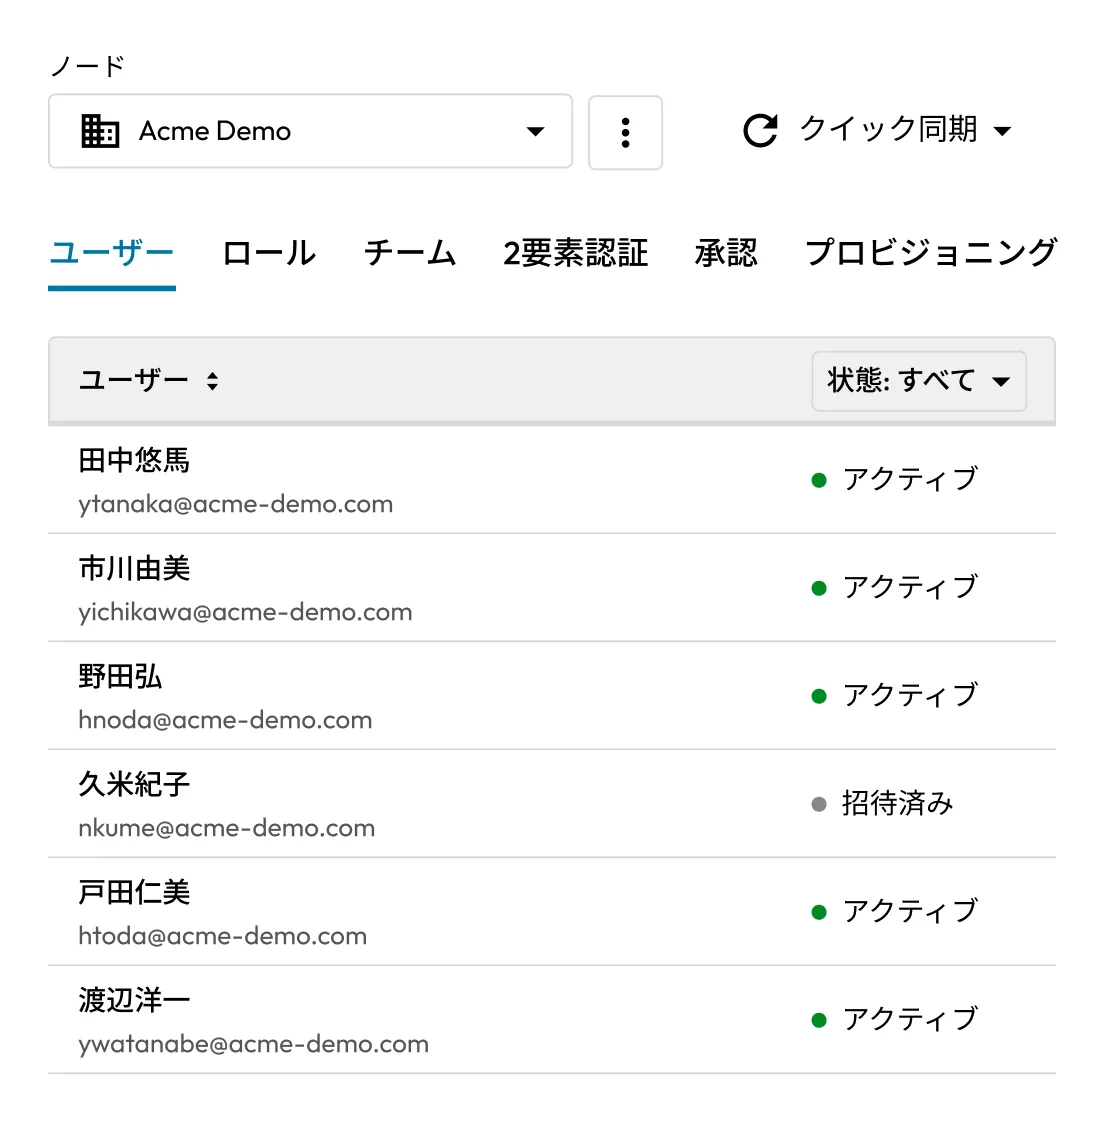
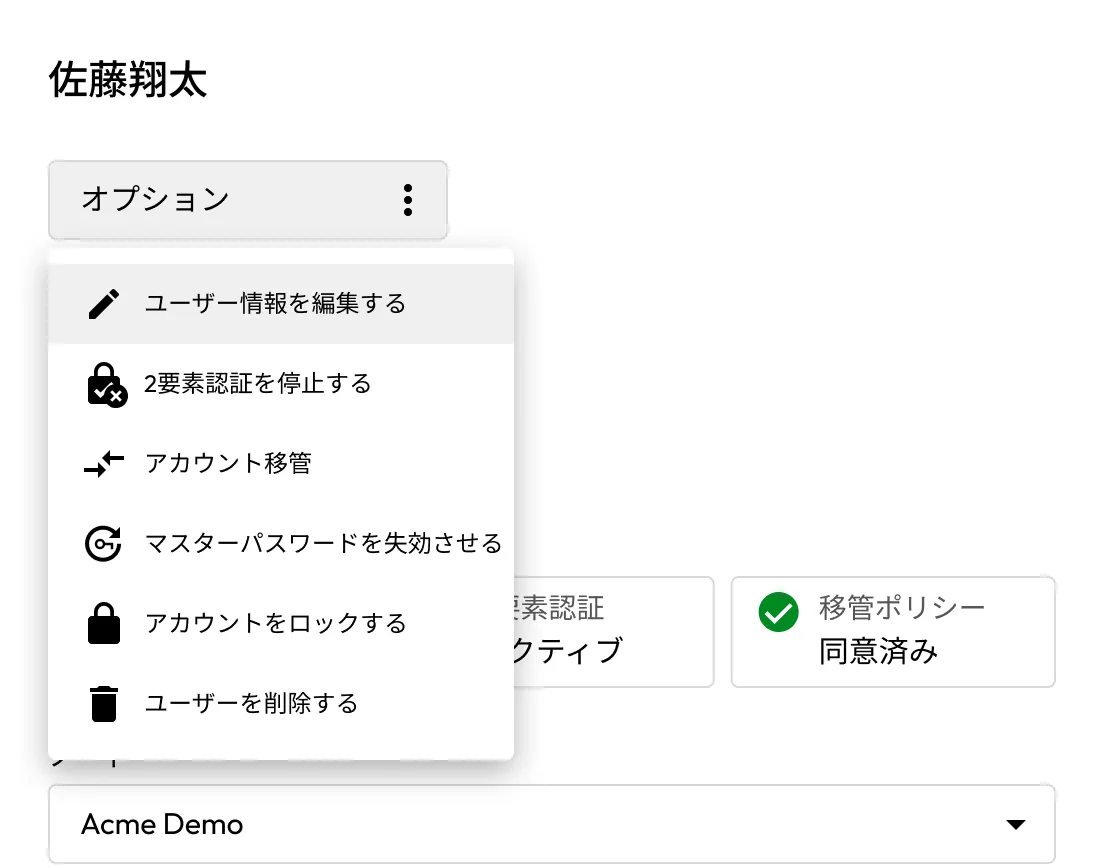
Govern access to privileged resources, such as credentials, servers, databases and cloud identities, all while maintaining Keeper's zero-knowledge encryption model. Through SailPoint, your team can manage identity lifecycle and enforce least-privilege access across Keeper's entitlement structure, including nodes, roles, teams, folders, and individual records, ensuring the right identities have access to the right resources at the right time.