Extend access into Teams with zero-knowledge encryption
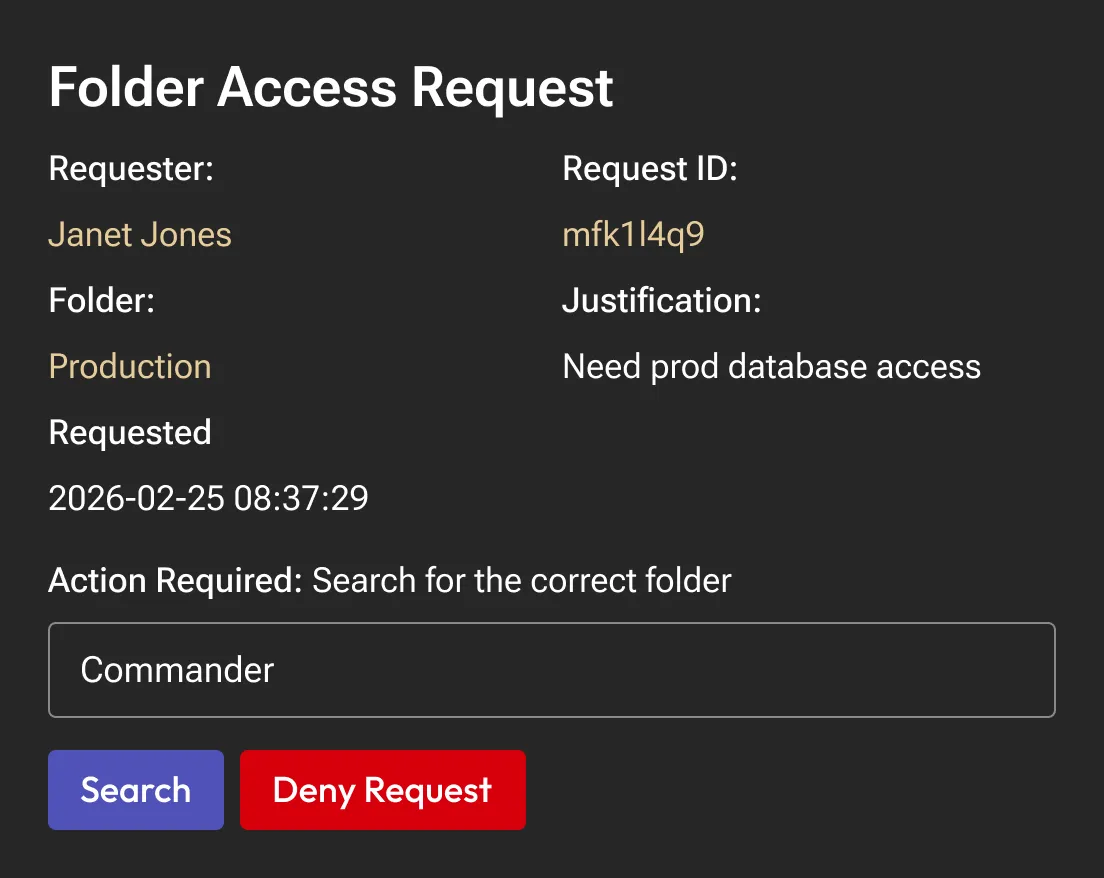
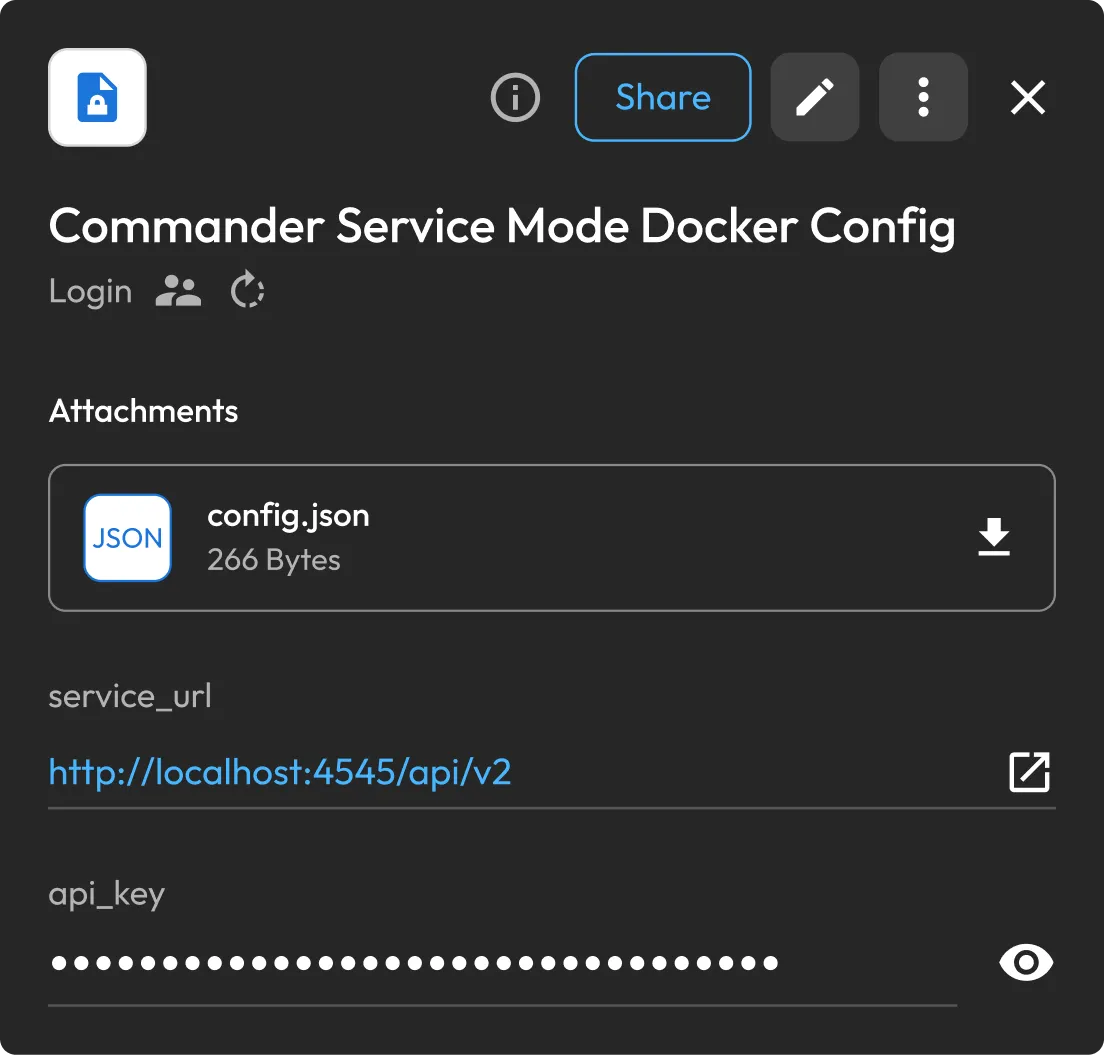
Keeper’s Teams workflow is deployed within your own environment, allowing organisations to extend secure access into Microsoft Teams while adhering to Keeper’s zero-knowledge architecture. The Teams agent and Keeper Commander® run in Docker containers hosted in your infrastructure and communicate with the Microsoft Teams cloud over an outbound connection you control.
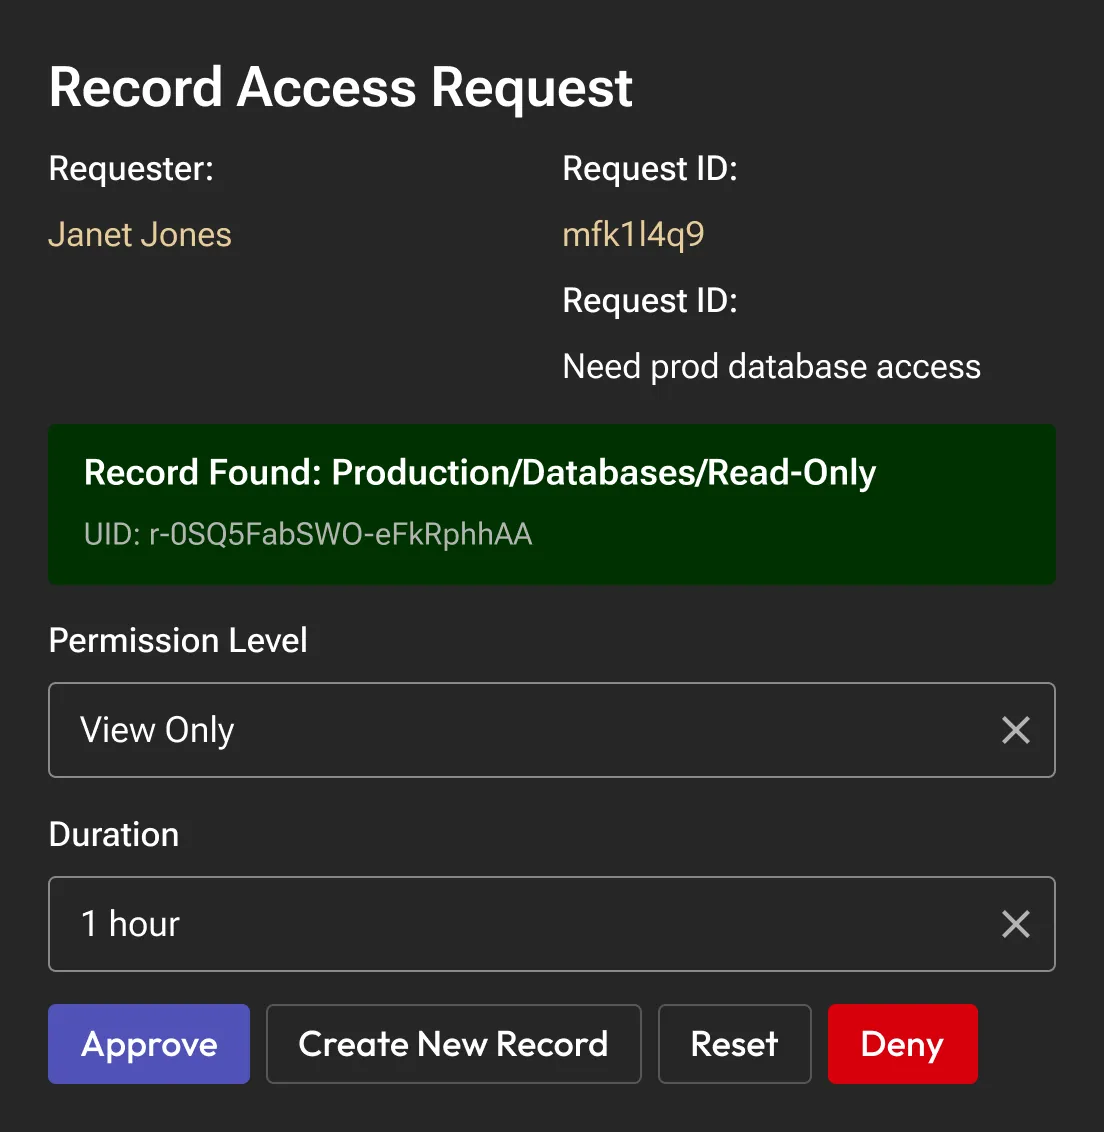
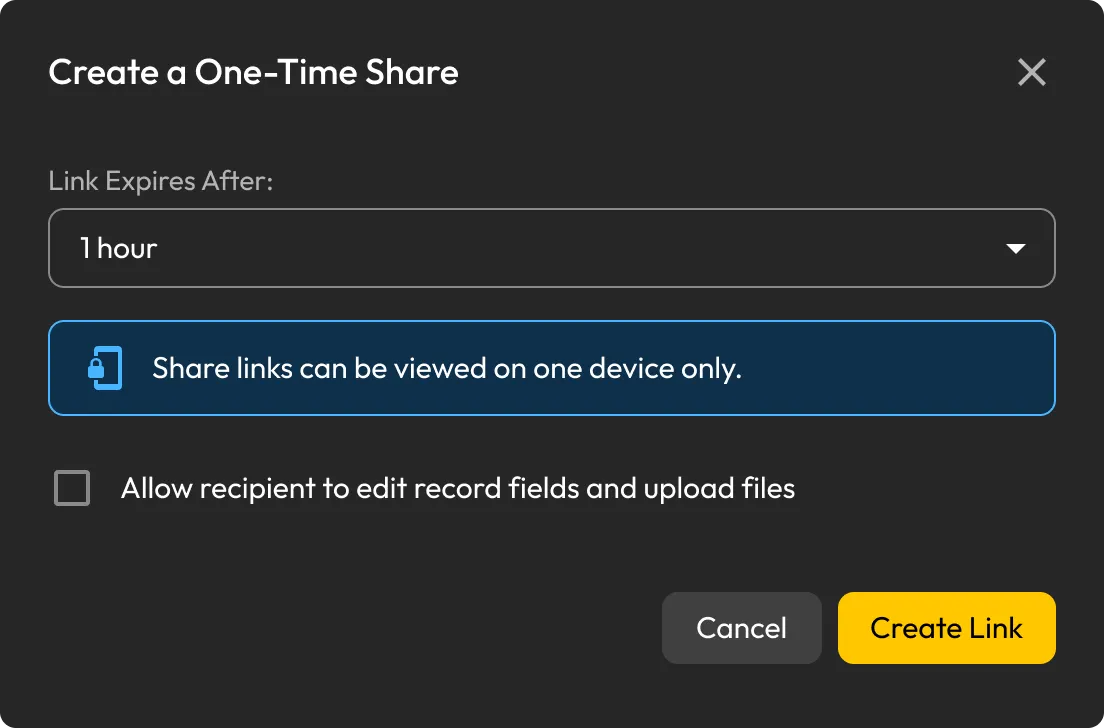
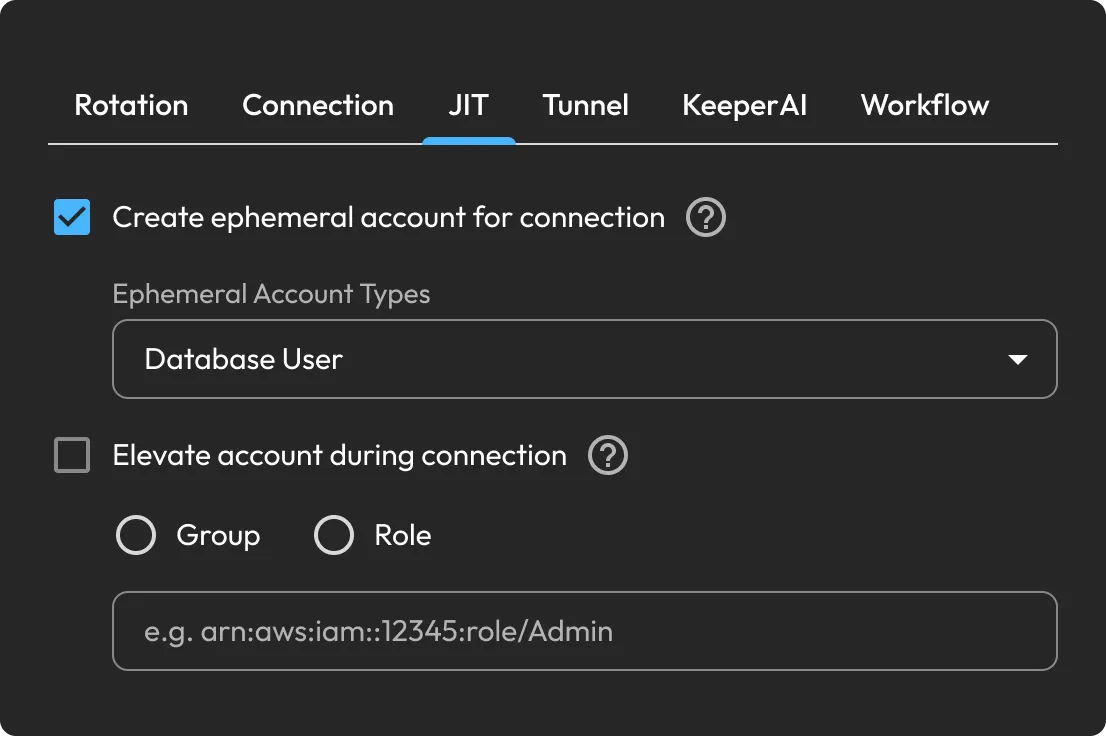
Encryption keys remain under your control, ensuring secrets stay encrypted throughout the workflow and no one — not even Keeper — can access any data. The Teams workflow helps organisations implement Zero Standing Privilege (ZSP) by allowing users to request temporary access, receive approvals and automatically enforce time-limited permissions without exposing credentials. Since the Teams app is published only to your organisation’s private app catalog, the app is not listed in the public Microsoft Teams store.