Zero Standing Privilege

Achieve zero standing privilege with KeeperPAM®

Keeper helps organisations eliminate standing privileges by replacing permanent administrative rights with Just-In-Time (JIT) access, ephemeral credentials and automated credential rotation - all from a zero-trust, zero-knowledge platform.
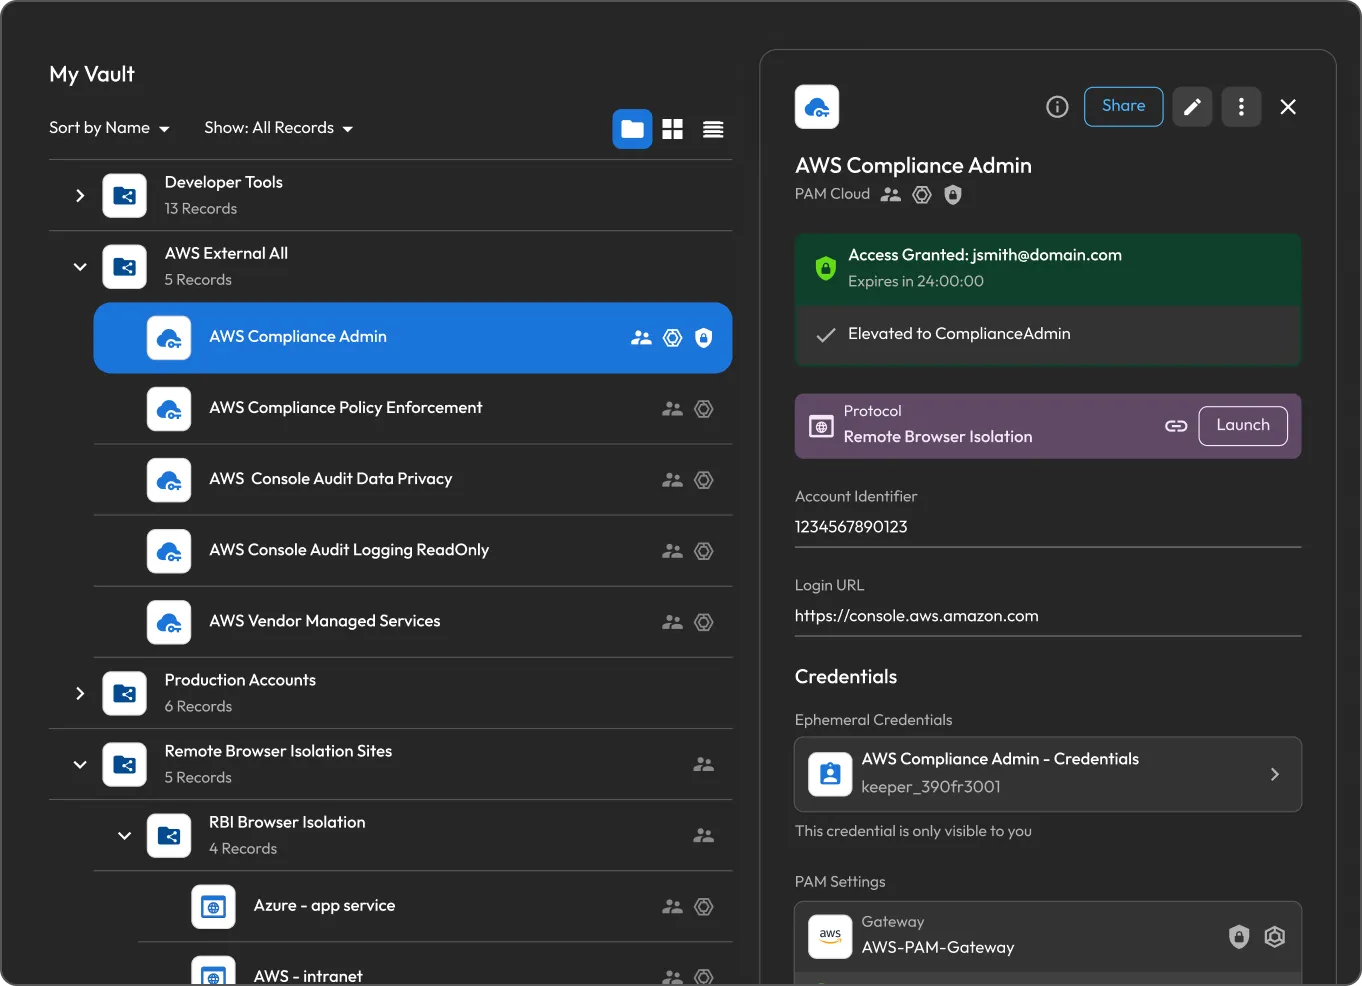
KeeperPAM interface showing temporary AWS Compliance Admin access with ephemeral credentials, 24-hour expiration and Remote Browser Isolation.

Why standing privileges put organisations at risk

Large attack surface

Every account with permanent privileged access is a target. If one gets compromised, the attacker can reach critical systems and sensitive data.

Privilege creep

Users accumulate access and keep it after projects end. Access that was meant to be temporary becomes permanent, and over time, more people hold more access than their work requires.

Lateral movement

Attackers can use stolen credentials to move across environments and escalate privileges, potentially leading to a wider breach.

Hard to prove least privilege

Auditors expect least privilege to be enforced. Proving that no one holds unnecessary standing access is difficult without a system built to enforce it.

How KeeperPAM helps enforce zero standing privilege

Grants just-in-time access

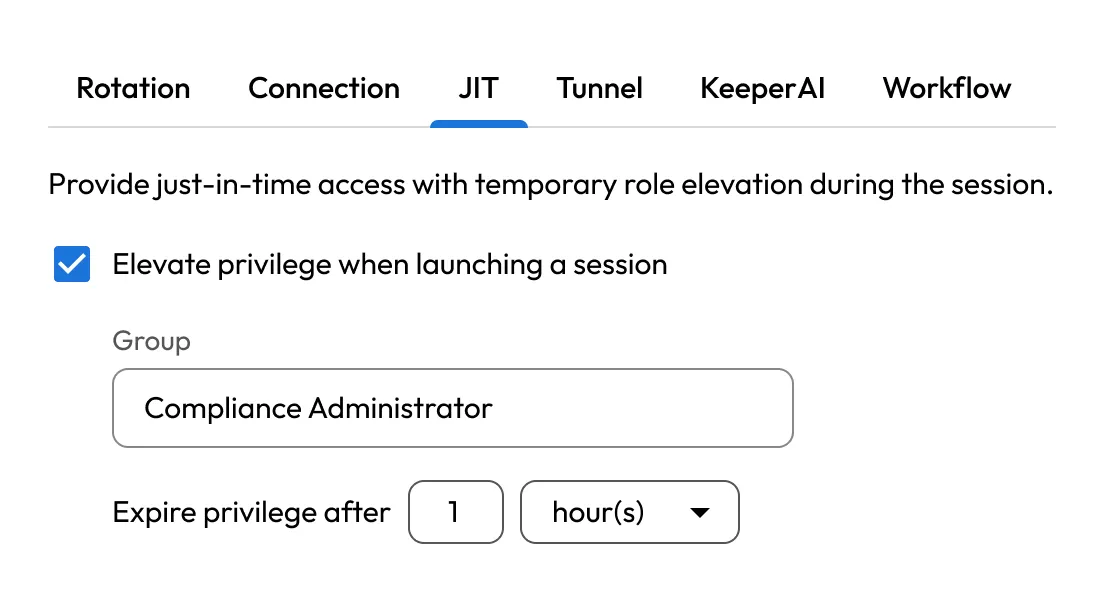
KeeperPAM eliminates standing privileges with JIT access. Users get the access a task needs, hold it only for a set window and lose it automatically when that window closes.

Keeper JIT settings granting temporary Compliance Administrator privileges when a session launches, with elevated access set to expire after one hour.

Requires approval before access is granted

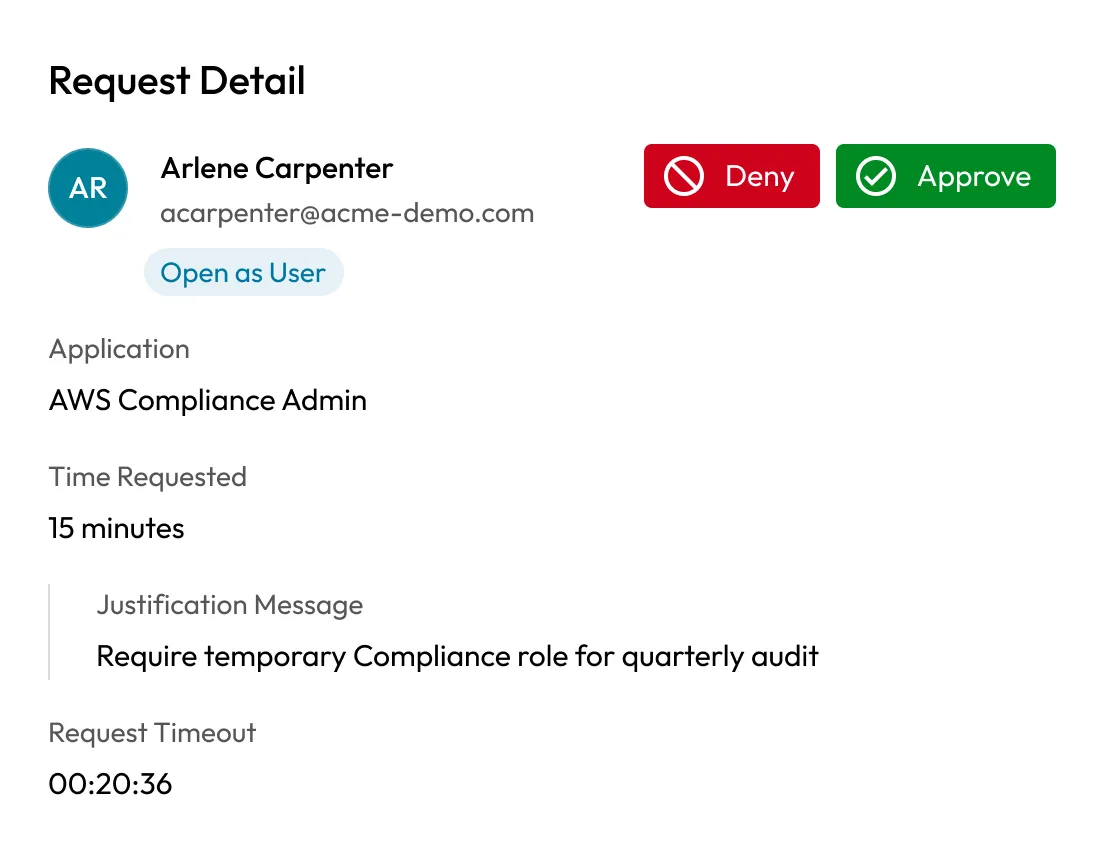
Privileged access doesn’t have to be automatic. KeeperPAM can route each request through an approval workflow, so a designated approver can authorise access before it’s issued. Requests may require justification and MFA, and every request, approval and denial is captured in an audit trail.

Keeper access request showing a temporary AWS Compliance Admin role requiring approval, with requested duration, justification and options to approve or deny access.

Injects credentials without exposing them

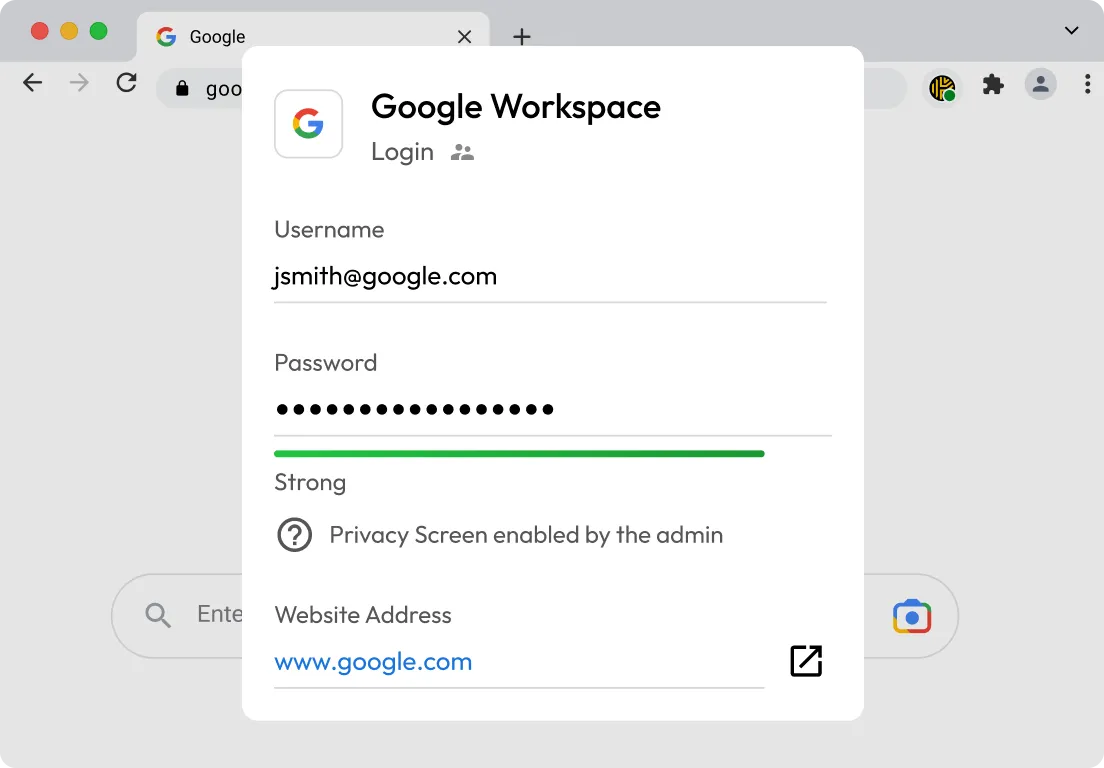
Keeper retrieves the stored credential from the Keeper Vault at session launch and injects it into the session through the customer-deployed Keeper Gateway. The user never sees or handles the underlying secret, reducing the risk of stolen or reused credentials.

Keeper credential injection securely fills a Google Workspace login while keeping the password masked and hidden from the user.

Provisions temporary accounts and elevates roles on demand

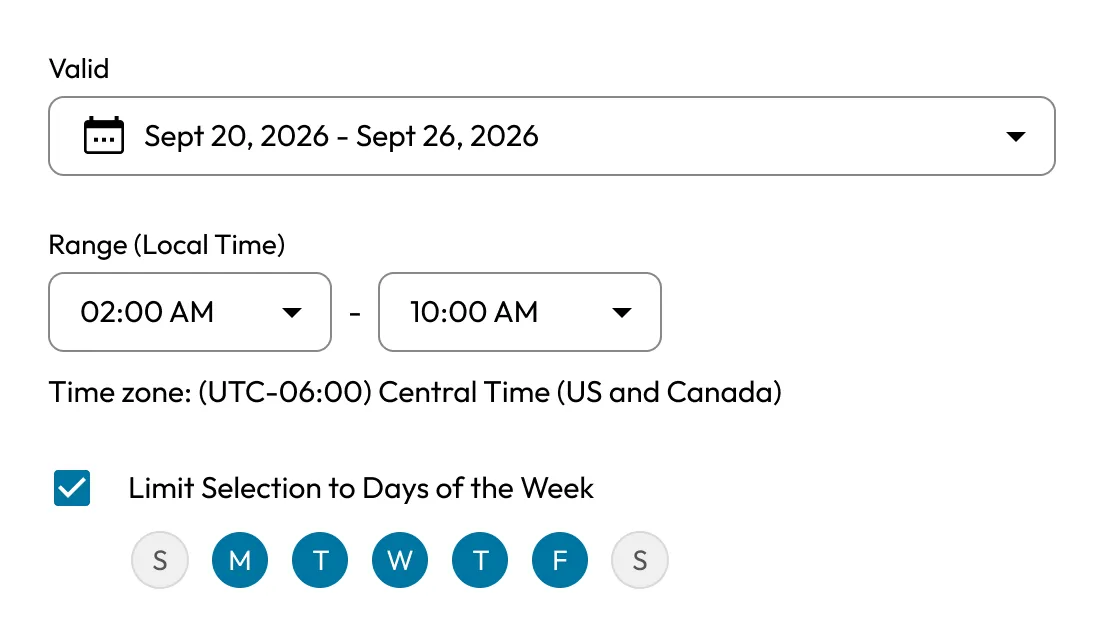
Rather than leave privileged accounts in place, Keeper can create short-lived accounts on the target system for the session and remove them when the session ends. For cloud platforms and endpoints, Keeper can elevate a user’s role for the duration of the task and then automatically remove it.

Keeper access schedule defining approved dates, hours and weekdays for provisioning temporary accounts and elevating roles on demand.

Rotates and retires credentials automatically

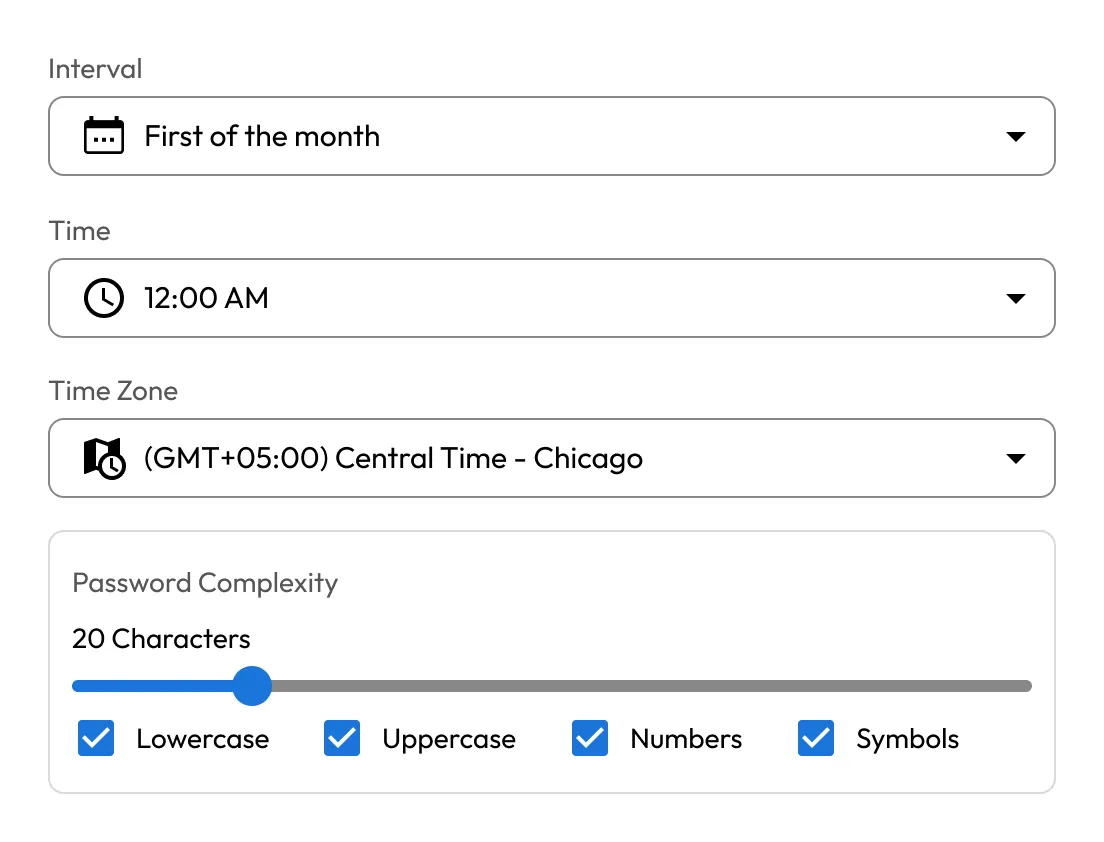
Keeper discovers privileged accounts and rotates their credentials on demand or on a set schedule, so no secret sits unchanged for months.

Keeper credential rotation settings showing automated monthly password rotation with configurable timing and password complexity for securely rotating and retiring credentials.

Enforces zero trust across modern infrastructure

The Keeper Gateway brokers access via an outbound-only connection to the Keeper Cloud, so no inbound ports are exposed and target systems remain unexposed. Least privilege is enforced consistently across on-premises infrastructure, hybrid environments, cloud platforms and databases.

Benefits of zero standing privilege with Keeper

Keep teams productive

Zero standing privilege doesn’t have to slow work down. Users launch sessions to authorised targets and work with their own native tools — SSH, RDP and database clients — while approvals move quickly without a VPN sitting in the way.

Reduce the overhead of managing privileged accounts

Standing accounts and shared credentials must be inventoried, provisioned, rotated and deprovisioned — typically manually. Keeper automates that lifecycle, creating access when it’s requested and revoking it when a task is completed.

Simplify audits and reporting

Every access request, approval and session is automatically logged, with built-in reporting. Instead of manually collecting evidence during audits, security teams have a ready-made trail that demonstrates controls for frameworks such as ISO 27001, HIPAA and SOC 2.

Modernise without legacy PAM

Keeper deploys via a lightweight gateway and zero-trust architecture with no VPNs or inbound firewall changes. Its unified platform helps organisations achieve zero standing privilege without rebuilding an entire network.

Move to zero standing privilege with Keeper

Frequently asked questions

How does Keeper eliminate standing privileges?

KeeperPAM replaces standing privileges with JIT access, provisions credentials only when needed and can create and remove temporary accounts automatically during each session. Requests can be routed through approval workflows, and any remaining static credentials are discovered and rotated on a schedule or on demand, reducing persistent access across environments.

How is zero standing privilege different from least privilege?

Least privilege focuses on limiting the scope of access, giving each user only the permissions necessary for their role. Zero standing privilege takes that further by also limiting the duration, so necessary privileges are granted temporarily and removed automatically. In simple terms, JIT access is what makes zero standing privilege possible.

Does zero standing privilege with Keeper require a VPN?

No, Keeper brokers access through the Keeper Gateway using outbound-only connections and a zero-trust architecture, so JIT access can be delivered without a VPN or inbound firewall changes.

How does zero standing privilege support compliance?

By enforcing least privilege in practice and capturing detailed audit trails of privileged activity, Keeper gives teams concrete evidence for audits and reviews. This helps address privileged access controls in frameworks such as ISO 27001, HIPAA, SOC 2 and NIST 800-53.

Withdraw Cookie ConsentWe value your privacy

We use cookies on our site to give you the best browsing experience, serve personalised ads about our products and content, and analyse website traffic. To learn more, please refer to our Privacy Policy.

Sign up for a Free Trial

Buy Now