Enhance Keeper Vault governance with SailPoint

Bring identity governance to Keeper with SailPoint IdentityIQ and Identity Security Cloud. Aggregate accounts and entitlements, provision vaults, manage privileged access and offboard users from SailPoint while preserving Keeper's zero-knowledge encryption.

Govern and manage privileged access

Govern access to privileged resources, such as credentials, servers, databases and cloud identities, all while maintaining Keeper's zero-knowledge encryption model. Through SailPoint, your team can manage identity lifecycle and enforce least-privilege access across Keeper's entitlement structure, including nodes, roles, teams, folders, and individual records, ensuring the right identities have access to the right resources at the right time.
Full lifecycle control, one connector

Entitlement aggregation

Collect and list the entitlements available in your Keeper organization, with their permissions.

  • Roles, teams and nodes
  • Privileged resources with their permission levels
  • Shared folders, classic and nested
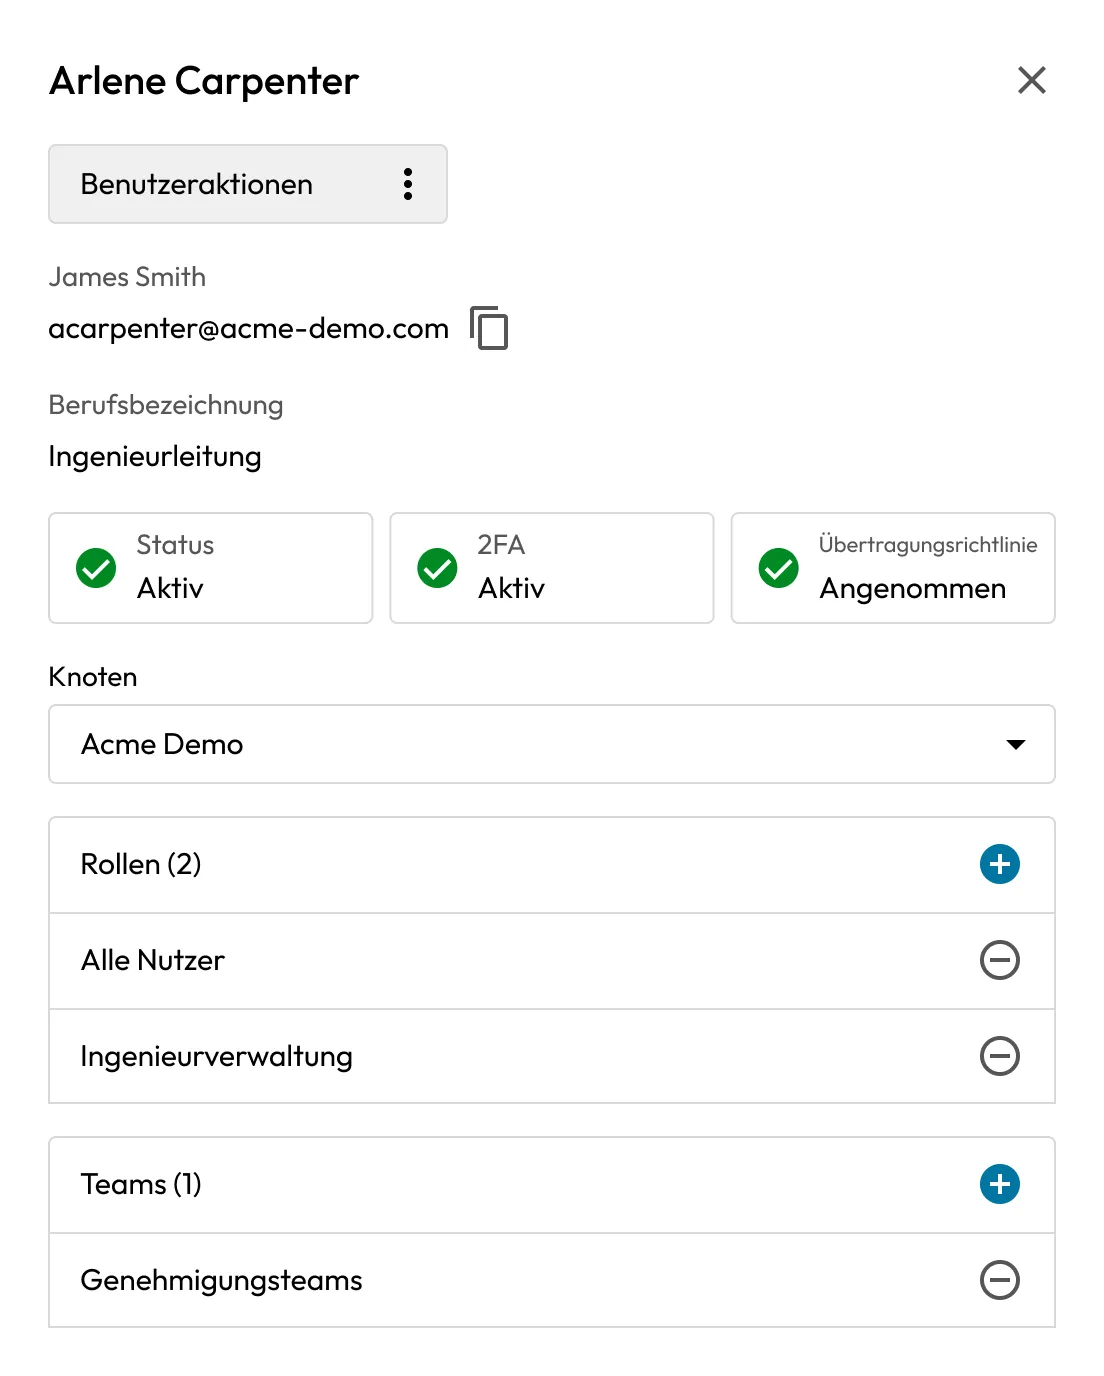
Keeper Admin Console showing user details, account status, assigned roles and team membership.

Account aggregation

List users from your Keeper organization and map each one to their existing Keeper Vault entitlements.

  • List users in SailPoint by email
  • Map users to existing Keeper Vault entitlements
  • View a user's assigned entitlements
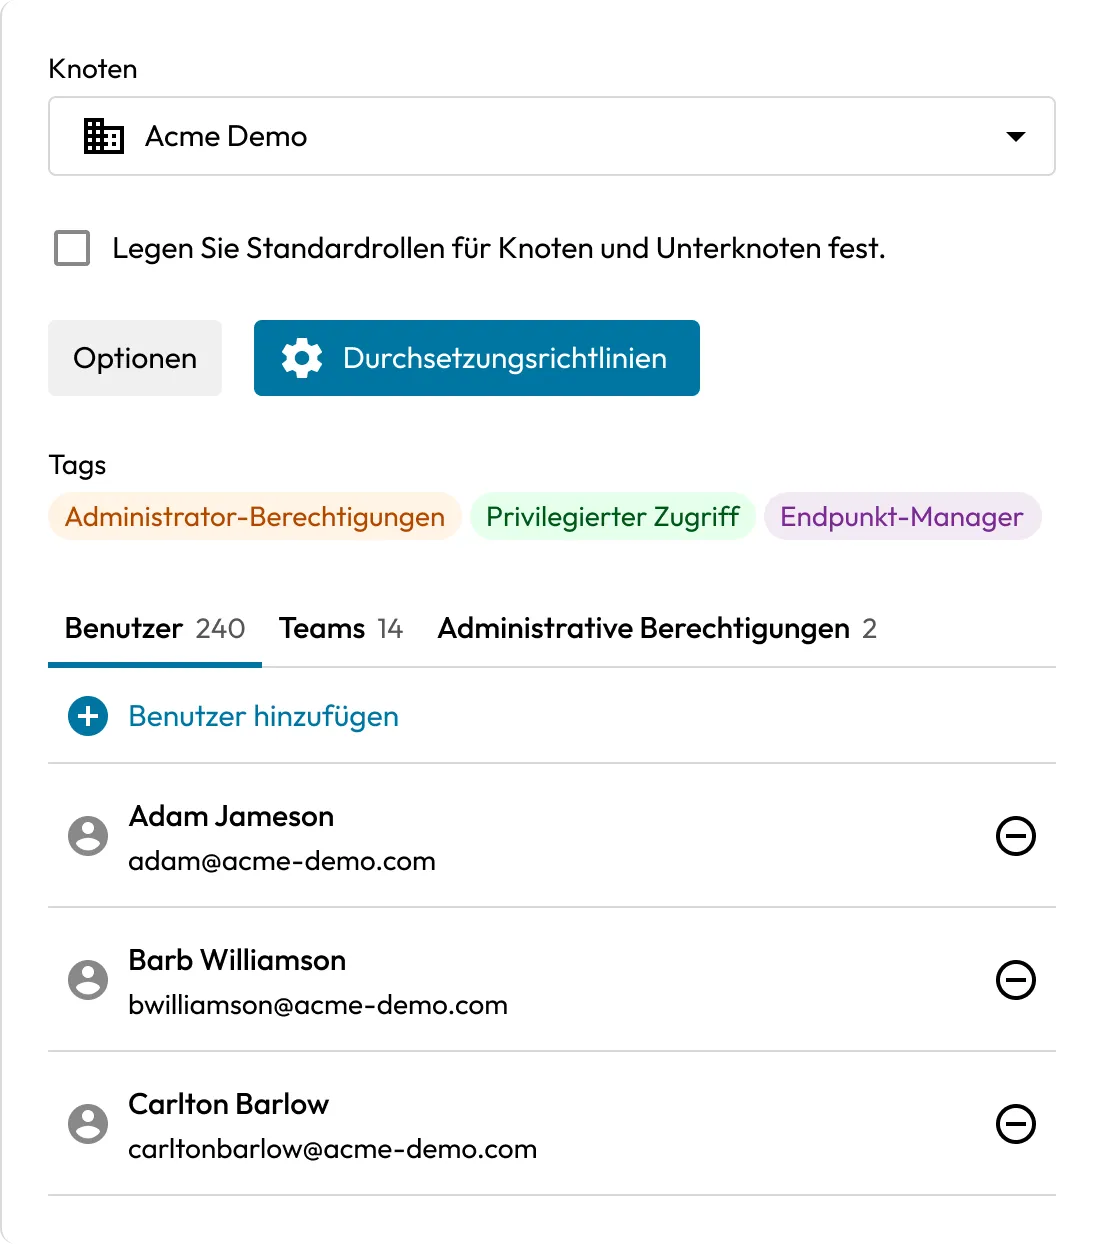
Keeper Admin Console showing role settings, enforcement policies, tags and assigned users.

Provision and assign

Invite users from SailPoint, provision a Keeper Vault for each and assign their access.

  • Invite a user and provision their Keeper Vault
  • Assign available roles, teams and nodes
  • Grant access to privileged resources in the vault based on the assigned permission level
  • Offboard
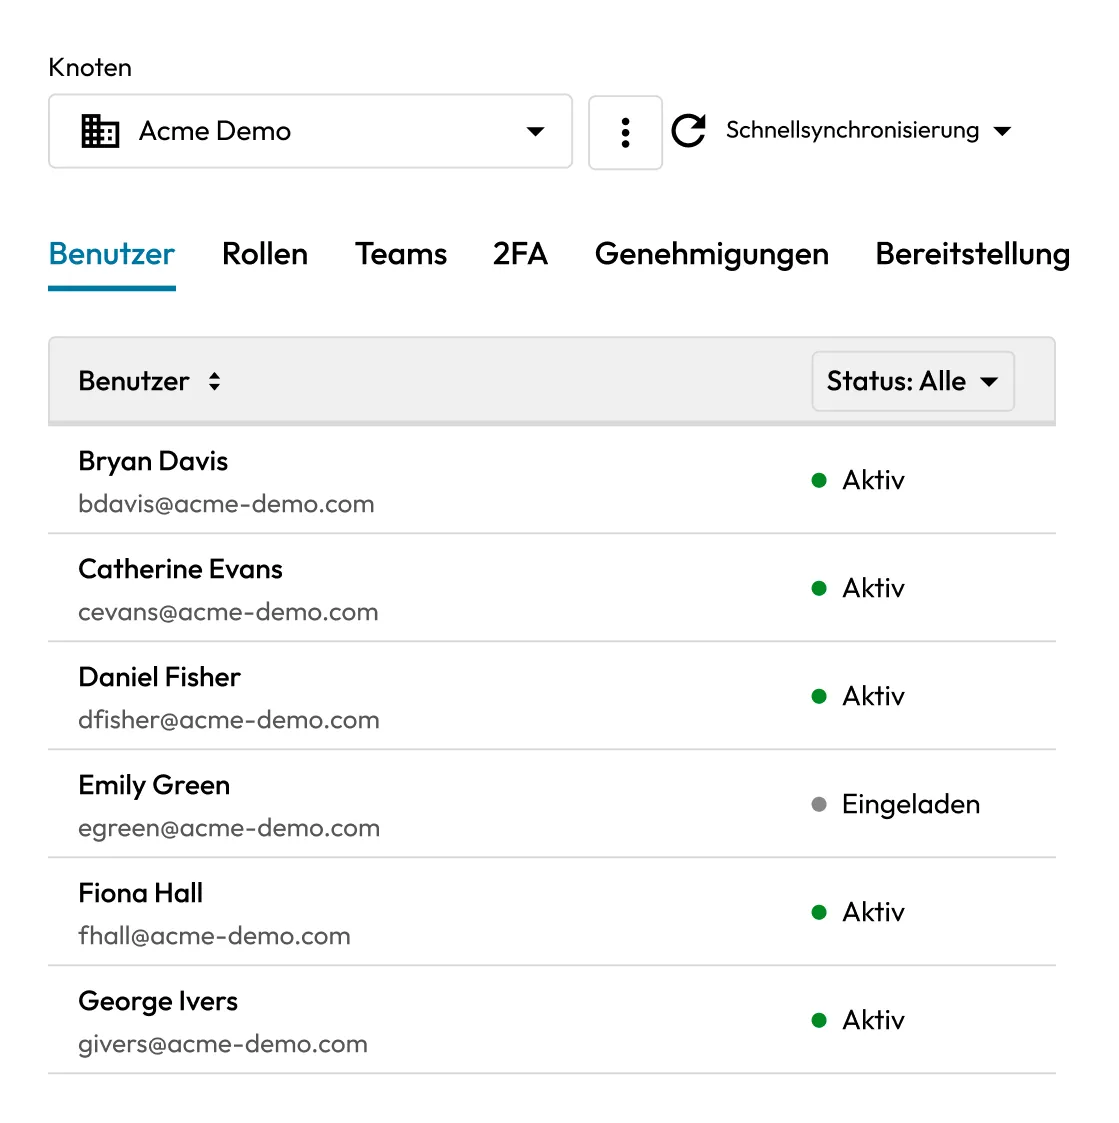
Keeper Admin Console showing a list of users with active and invited account statuses.

Enable, disable, offboard

Enable, disable or delete Keeper accounts and keep user details in sync.

  • Enable or disable access to the Keeper Vault
  • Update a user's name and email
  • Delete an account — vault contents are transferred to the designated user and the account is removed
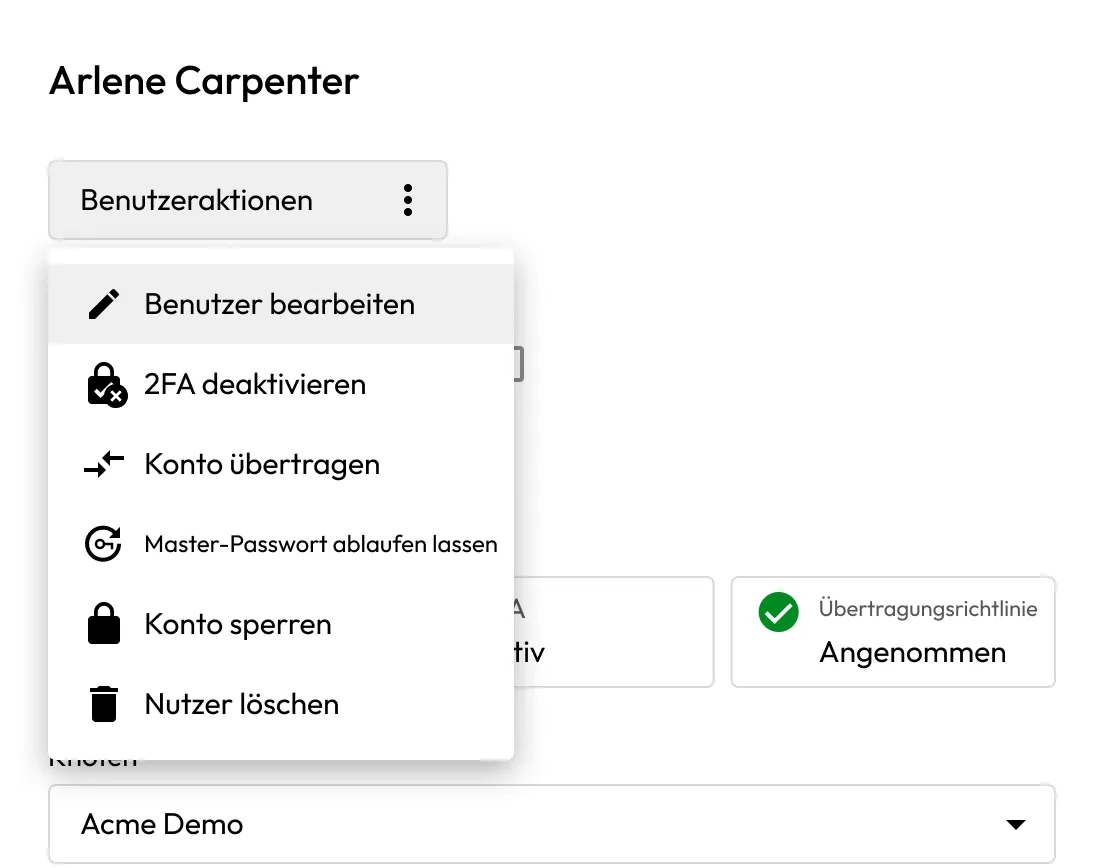
Keeper Admin Console showing user management actions, including editing, disabling 2FA, transferring, locking and deleting accounts.

How a governed request works

Request access in SailPoint

An engineer requests access to "Production PostgreSQL" in SailPoint by selecting the entitlement associated with the database's Keeper record.

User activates their vault

SailPoint routes the request to the designated approver based on your configured approval policies.

Assign the entitlement

Once approved, the connector grants access to the database's Keeper record at the assigned permission level. The record appears in the engineer's vault.

Review and certify access

Review the database entitlement through SailPoint access certifications. Confirm the engineer still needs access or revoke the entitlement when it is no longer required.

Identity governance with zero-knowledge security

SailPoint manages Keeper accounts and entitlements through Keeper Commander Service Mode running on your infrastructure. The connector is restricted to approved governance operations, preserving Keeper's zero-knowledge encryption.

What you'll need before you start

1. Keeper Enterprise

Administrative access to manage users, teams, roles and sharing across your organization.

2. Commander Service Mode

API v2 running and reachable from SailPoint, set up in one flow with sailpoint-app-setup.

3. SailPoint ISC admin

Permissions to create sources, configure correlation and run aggregations in Identity Security Cloud.

Put Keeper access under governance

Häufig gestellte fragen

Does this expose my secrets to SailPoint?

No, SailPoint never reads vault contents. Every operation runs through Commander Service Mode on your own infrastructure, and its allowlist blocks secret-bearing commands like get, export and find-password. Keeper's zero-knowledge model stays intact.

How does SailPoint connect to Keeper?

SailPoint connects to Keeper through  Keeper Commander running in Service Mode on your infrastructure, using API v2. SailPoint never talks to Keeper directly. If Commander runs on a private network, expose it via ngrok or Cloudflare Tunnel and point the source to that HTTPS URL.

What can the connector provision?

The connector can provision the full user lifecycle — invite, enable, disable and delete — plus roles, teams and record and folder shares. You decide which of these the connector may manage when you run setup; anything you disable is rejected with an HTTP 403.

Which entitlement types are supported?

There are five entitlement types supported: nodes, teams, roles, folders and records. Folder and record entitlements carry their own permission level and work with both classic and nested shared folders.

What happens when I offboard a user?

The connector transfers the departing user's vault to the target account you set during setup, then removes their Keeper account. Nothing they held is lost; it moves to the transfer target first.

Einverständnis zur Cookie-Nutzung widerrufenWir schätzen Ihre Privatsphäre

Wir verwenden Cookies auf unserer Website, um Ihnen das beste Browser-Erlebnis zu bieten, personalisierte Anzeigen zu unseren Produkten und Inhalten zu bieten und den Website-Datenverkehr zu analysieren. Um mehr zu erfahren, lesen Sie bitte unsere Datenschutzrichtlinie.

Für die kostenlose Testversion anmelden

Jetzt kaufen