Secure privileged access across Google Cloud with Keeper

Discover GCP resources and principals, rotate cloud and Google Workspace credentials, grant approved time-bound access through Google identity and keep Google Cloud Secret Manager synchronized from Keeper Vault—all through KeeperPAM and a Gateway in your environment.

Keeper integration graphic showing the Google Cloud logo connected to the Keeper logo.

Discover, control and synchronize your GCP environment

KeeperPAM brings discovery, identity-based just-in-time access, credential rotation and secrets synchronization into one governed lifecycle for Google Cloud infrastructure and identities.

How Keeper works with Google Cloud

Discover GCP resources and principals

Keeper Gateway uses the GCP PAM Configuration to identify Compute Engine VMs, Cloud SQL instances, Managed Microsoft AD and principals found in project IAM policies. Customizable rules determine which findings become managed KeeperPAM records.
Grant time-bound access through Google identity

Keeper Privileged Cloud grants approved group membership, roles or entitlements through Google identity for a defined access window. Users continue through the target platform's normal authentication flow, and Keeper removes the temporary assignment automatically when access expires.

Rotate Google Cloud credentials

Rotate accounts linked to Compute Engine, Cloud SQL and Managed Microsoft AD, along with Google Workspace principals discovered in project IAM policies. Workspace password rotation uses a service account with domain-wide delegation and an authorized Google administrator.

Capabilities for securing Google Cloud

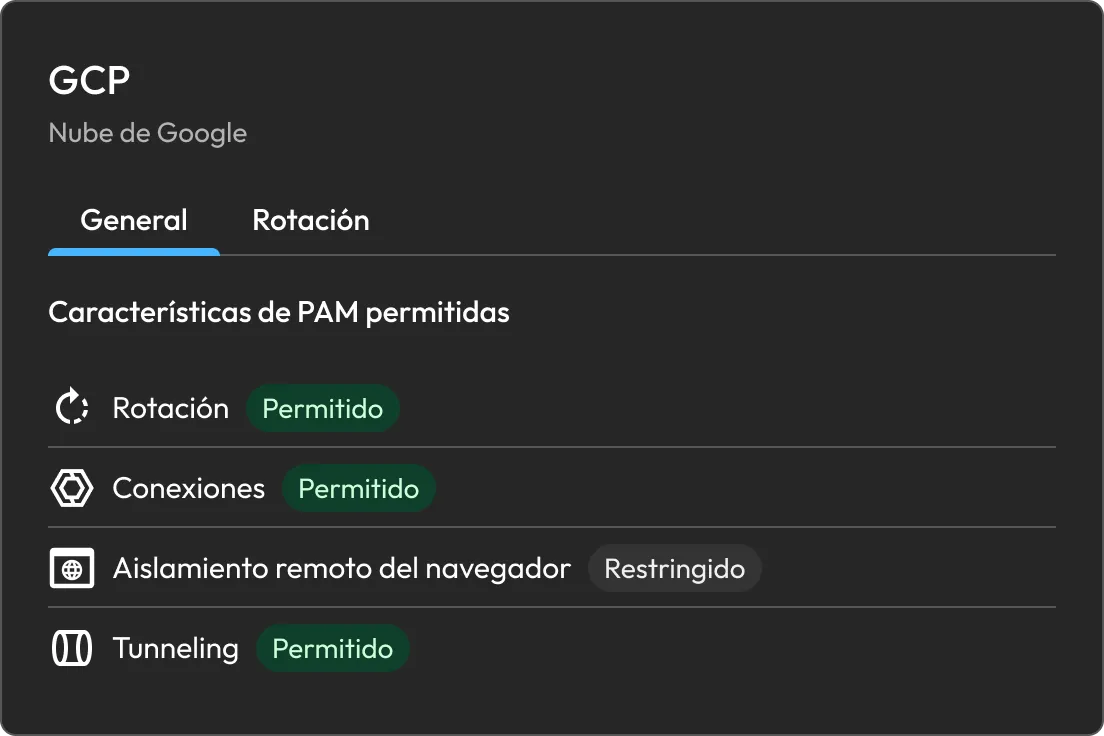
KeeperPAM Google Cloud configuration showing allowed rotation, connections and tunneling, with Remote Browser Isolation restricted.

Model resources in KeeperPAM

Represent Compute Engine as PAM Machine, Cloud SQL as PAM Database, Managed Microsoft AD as PAM Directory and Google Workspace principals as PAM User records.

Keeper integration icons for Ansible, Bitbucket, Docker, GitHub Actions, GitLab, Heroku and Jenkins.

Approve and expire cloud access

Configure JIT and Workflow on a PAM Cloud resource to set the target group or role, approval path, access duration, justification and ticket requirements.

Discover and onboard at scale

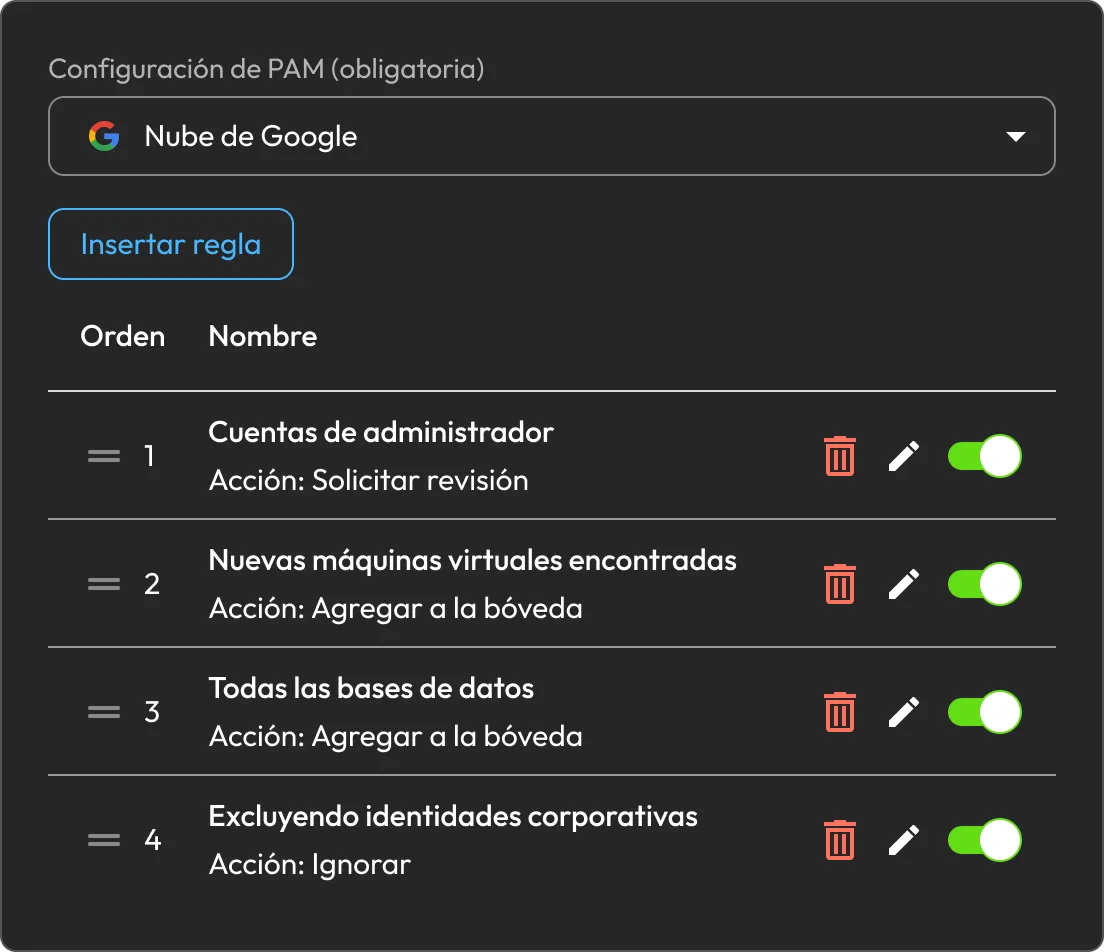
Use rules to add, ignore or review findings before they enter a Shared Folder, then run deeper discovery to identify local users and services on managed resources.

KeeperPAM Google Cloud configuration showing enabled discovery rules for admin accounts, virtual machines and databases.
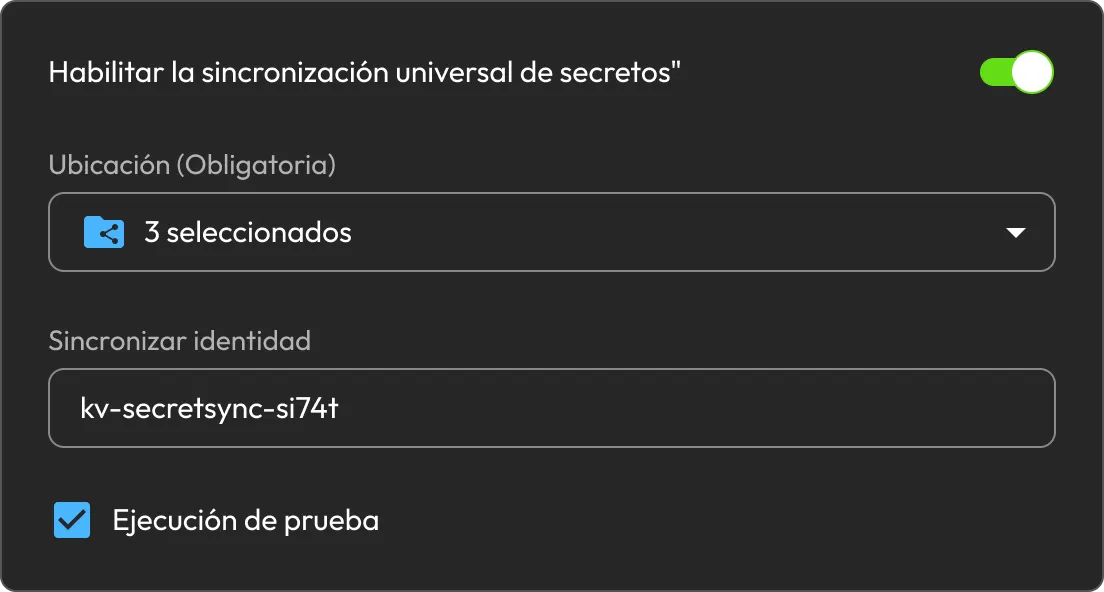
Keeper Universal Secrets Sync settings showing enabled synchronization, selected locations, sync identity and dry run option.

Keep Secret Manager synchronized

Universal Secrets Sync sends changed Keeper records to Google Cloud Secret Manager through Keeper Gateway, preserving metadata tags for the record UID, type and title.

Keeper Gateway authenticates with a dedicated service-account Sync Identity and writes directly to Google Cloud. Plaintext never crosses Keeper's cloud infrastructure, and each result is audited.

Why teams connect Keeper and Google Cloud

Reduce standing privilege

Grant GCP groups, roles or entitlements only for an approved window and remove them automatically when access expires.

Discover cloud assets

Identify Compute Engine, Cloud SQL, managed directories, principals and local accounts through Keeper Gateway.

Rotate supported credentials

Apply rotation to GCP resource accounts and Google Workspace principals using scoped service-account access.

Keep applications current

Update a secret once in Keeper Vault and push the change directly to Google Cloud Secret Manager through Keeper Gateway.

Bring Google Cloud privileged access under control

Preguntas frecuentes

How does Keeper provide just-in-time access to Google Cloud?

After approval, Keeper temporarily grants the mapped Google identity group membership, role or entitlement for the configured duration, then removes it automatically. Users continue through the cloud console, SSO, CLI or SDK workflow that evaluates that identity change.

What can Keeper rotate in Google Cloud?

Keeper supports accounts associated with Compute Engine, Cloud SQL and Managed Microsoft AD, plus Google Workspace principals. Workspace password rotation requires domain-wide delegation, the Admin Directory API scope and an authorized Google administrator.

What can Keeper Discovery find in GCP?

Keeper Discovery identifies Compute Engine VMs, Cloud SQL instances, Managed Microsoft AD, IAM principals and related local users or services. Rules can add, ignore or prompt for each finding before onboarding.

How does Universal Secrets Sync work with Google Cloud Secret Manager?

Keeper Vault remains the source of truth. When a linked record changes, Keeper Gateway uses the configured service-account Sync Identity to write the updated value directly to Google Cloud Secret Manager. Multi-folder sync, dry-run previews, metadata tags and audit logging are supported.

Retirar el consentimiento de cookiesValoramos su privacidad

Utilizamos cookies en nuestro sitio web para ofrecerle la mejor experiencia de navegación, brindar anuncios personalizados sobre nuestros productos y contenido, y analizar el tráfico del sitio web. Para obtener más información, consulte nuestra Política de privacidad.

Regístrese para una prueba gratuita

Comprar Ahora